
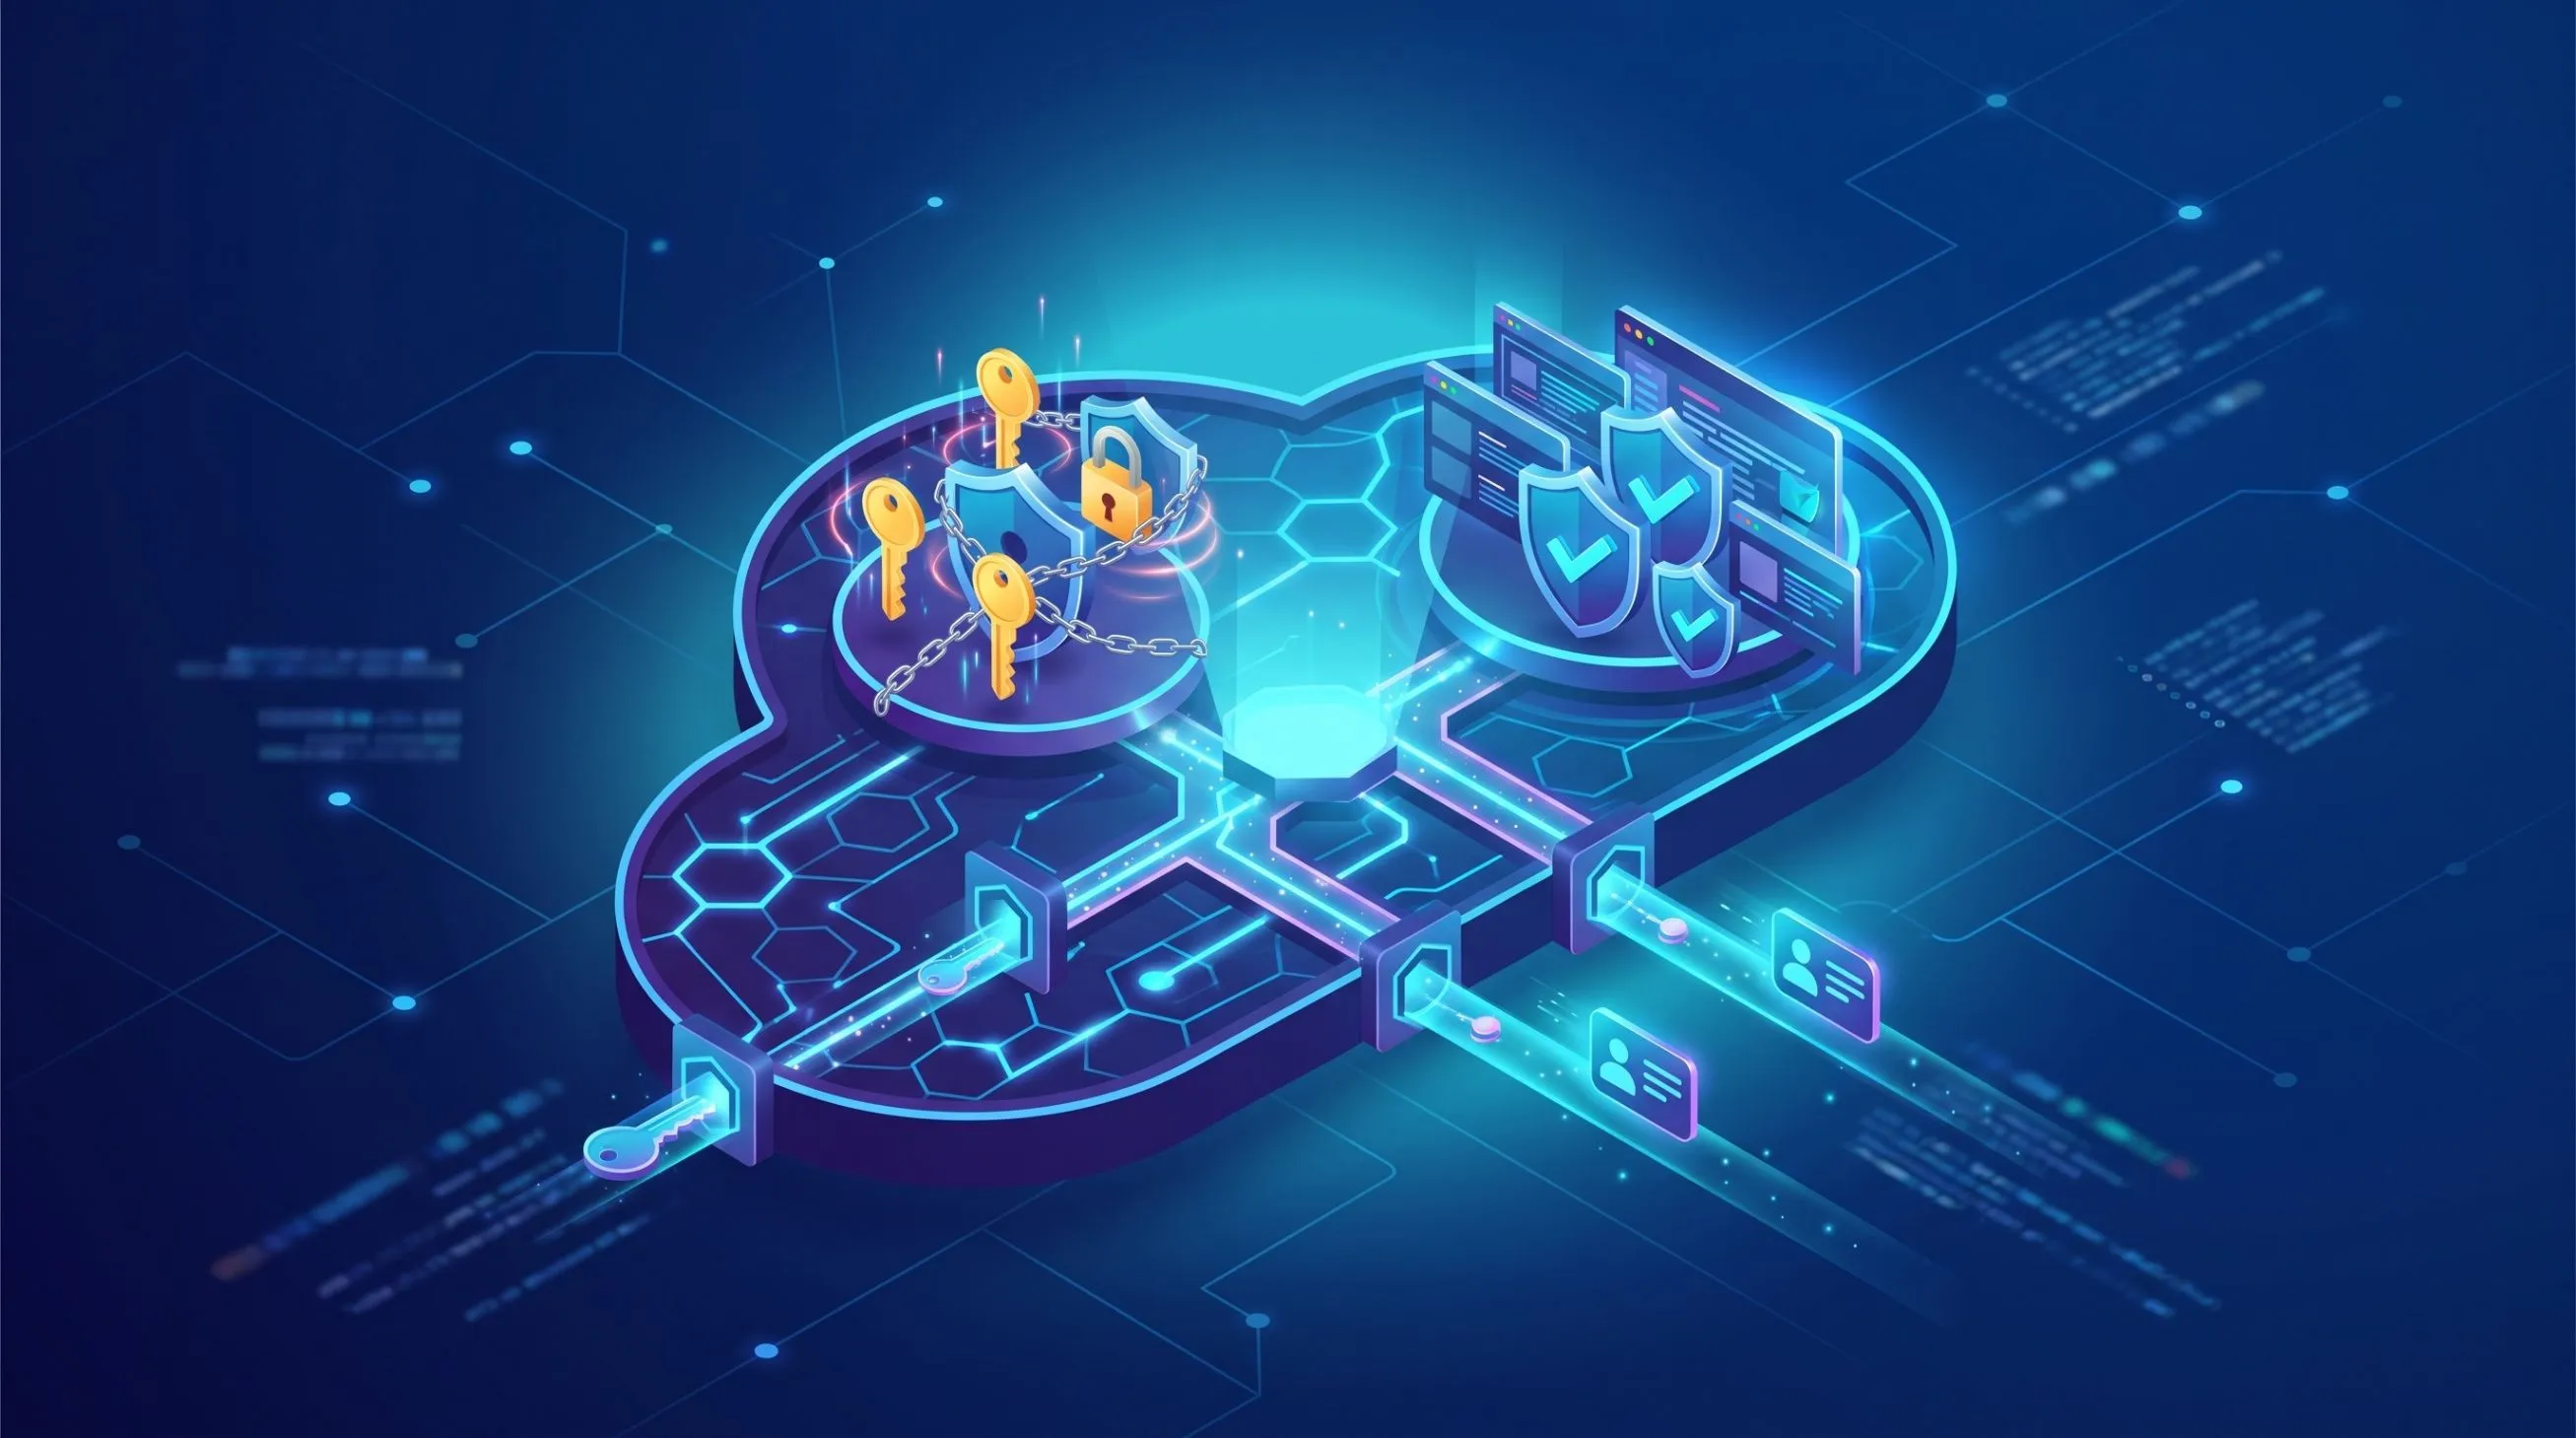
Cloud API Security and Secrets Management
Securing external and inter-service REST/GraphQL endpoints against injection attacks, unauthorized access, and credential leakage through API gateways, rate limiting, and centralized secrets vaults.
Series: Cloud Security (4 articles)
- …
- 3Cloud API Security and Secrets Management This article
Modern cloud-native architectures thrive on decoupling. Microservices, serverless functions, multi-tenant databases, and third-party integrations interact continuously through application programming interfaces (APIs). While this distributed paradigm drives agile development, it also reshapes the security perimeter: APIs are now the front door to cloud infrastructure, and the credentials governing them are high-value targets.
A vulnerability in an API endpoint or a single leaked access token can lead to full-scale infrastructure compromise. Securing cloud applications requires a unified approach that hardens API interfaces and enforces automated, lifecycle-driven secrets management.
Part 1: Hardening Cloud APIs
Cloud APIs typically span external entry points (public ingress via API Gateways) and internal service-to-service communication (east-west traffic). Securing them requires defense-in-depth across authentication, authorization, and network controls.
1. Robust Authentication & Granular Authorization
Weak or broken authentication remains a primary vector in API breaches (notably OWASP API1: Broken Object Level Authorization and API2: Broken Authentication).
- Standardized Token Workflows: Rely on industry-standard protocols such as OAuth 2.0 and OpenID Connect (OIDC). Avoid rolling custom authentication tokens or relying purely on static API keys for high-privilege operations.
- Stateless Tokens & Verification: For stateless architectures (e.g., using JSON Web Tokens / JWTs), enforce asymmetric signing (e.g., RS256 or ES256) rather than shared symmetric secrets. Ensure token verification checks expiration (
exp), issuer (iss), and audience (aud) claims strictly. - Fine-Grained Context Checks: Authentication only confirms who is calling; authorization dictates what they can access. Implement Policy-as-Code engines (such as Open Policy Agent / OPA) or attribute-based access control (ABAC) to validate that user
Acannot query or mutate data belonging to tenantB.
2. Centralized Ingress via API Gateways
Directly exposing microservices or compute instances to the public internet expands the attack surface needlessly. Placing an API Gateway (e.g., AWS API Gateway, Kong, Apigee) at the network edge establishes a single control plane:
- Rate Limiting and Throttling: Guard against Denial of Service (DoS), brute-force attacks, and credential stuffing by setting token-bucket or sliding-window rate limits per IP, user, or API key.
- Schema Validation: Enforce strict OpenAPI/Swagger request validation directly at the gateway. Payloads containing unexpected parameters, excessive payload sizes, or improper data types are rejected before reaching backend logic.
- Web Application Firewall (WAF) Integration: Pair the gateway with a managed WAF to inspect incoming HTTP payloads for common web exploits, SQL/NoSQL injections, and malicious bot activity.
3. Mutual TLS (mTLS) for East-West Traffic
Perimeter security alone does not protect internal services if an attacker breaches the private network. In microservice environments (such as Kubernetes or container meshes):
- Implement Mutual TLS (mTLS) to enforce two-way cryptographic identity verification between services.
- Service meshes (e.g., Istio, Linkerd) or cloud-native service discovery mechanisms can automate certificate issuance and rotation, ensuring inter-service requests are fully encrypted and authenticated.

API Gateway Ingress Architecture
Part 2: Modern Secrets Management
A robust API layer is useless if database passwords, third-party API tokens, encryption keys, and service account credentials are leaked. Secrets management establishes how sensitive material is generated, stored, retrieved, and rotated throughout its lifecycle.
The Antipatterns to Avoid
- Hardcoded Credentials: Embedding secrets in source control (even private repositories) is the most frequent cause of automated credential scraping.
- Static Environment Variables: While better than hardcoding, passing long-lived secrets as plain-text container environment variables leaves them vulnerable to exposure via
/procinspections, crash dumps, or debugging logs. - Unencrypted Configuration Files: Committing
.envfiles or pushing unencrypted configuration artifacts into deployment containers.
Core Principles of Secrets Security
| Principle | Implementation Strategy | Benefit |
|---|---|---|
| Centralized Secret Vaults | Use dedicated KMS/Vault platforms (e.g., AWS Secrets Manager, HashiCorp Vault, Azure Key Vault). | Eliminates credential sprawl across repositories and deployment scripts. |
| Short-Lived Dynamic Credentials | Issue temporary credentials tied to workload identities rather than permanent API keys. | Limits exposure window; credentials expire automatically. |
| Automated Secret Rotation | Integrate automated rotation functions (e.g., Lambda-backed rotation) with target data stores. | Leaked credentials become useless after their rotation cycle. |
| Least-Privilege Vault Access | Restrict vault decryption keys using granular IAM policies and IP/VPC condition keys. | Prevents compromised services from accessing secrets outside their domain. |
1. Identity Federation Over Static Keys
Cloud providers provide identity mechanisms that eliminate long-lived access keys entirely:
- Workload Identity / IAM Roles: Compute workloads (containers, virtual machines, serverless functions) should assume IAM roles directly using instance profiles or OIDC federation.
- CI/CD Federation: Instead of storing permanent cloud provider keys inside GitHub Actions or GitLab CI, configure OpenID Connect (OIDC). The runner requests a temporary, short-lived federated token directly from the cloud provider during pipeline execution.
2. Guarding the Pipeline (Shift-Left Secrets Detection)
To prevent credentials from ever reaching repositories:
- Pre-commit Hooks: Use tools like
gitleaksortrufflehoglocally to block commits containing high-entropy strings or known token signatures. - Automated CI Scanning: Scan every pull request for accidentally exposed secrets. If a secret is detected, consider it burned immediately—rotating the key is the only reliable fix.
3. Secure Retrieval at Runtime
Applications should fetch secrets at runtime via secure, authenticated SDK calls or file-system mounts:
- CSI Secret Store Drivers: In Kubernetes environments, use the Secrets Store CSI Driver to mount secrets directly into container memory volumes from external vaults without persisting them to disk.
- In-Memory Decryption: Ensure decrypted secret strings are kept in memory only for the duration needed and never written to persistent application logs.

Shift-Left Security: Integrating Security into CI/CD Pipelines
Summary Checklist for Cloud Architectures
- Verify Identity Everywhere: Implement OAuth 2.0 / OIDC externally and mTLS internally.
- Standardize Gateway Ingress: Restrict backend access to managed API Gateways with active rate limiting and request validation.
- Eliminate Static Credentials: Replace long-lived keys with IAM roles, instance profiles, and OIDC federation.
- Automate Rotation: Configure cloud vaults to rotate database credentials and API keys on an automated schedule.
- Continuous Audit & Monitoring: Centralize API logs and secret access audit trails into a SIEM to flag anomaly spikes, unauthorized access attempts, and permission drifts.
Series: Cloud Security (4 articles)
- …
- 3Cloud API Security and Secrets Management This article
Enjoyed reading this content? Let the author know!
Your likes, comments, shares, and saves help creators reach more builders.

Loading recommendations
Loading article