
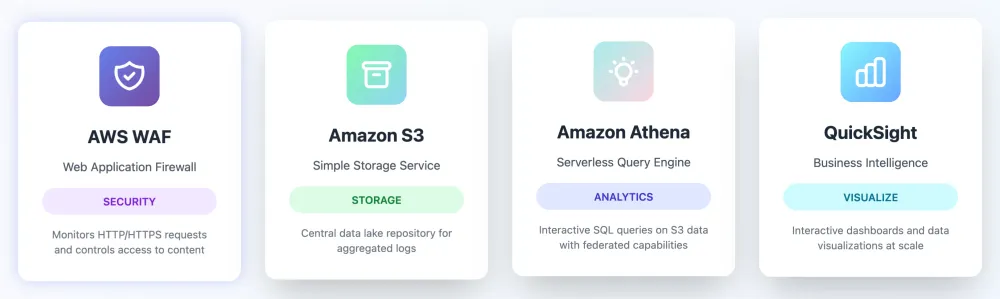
[Analytics Optimization] Under Attack? Switch to QuickSight: AI-Powered Threat Visibility 🚀🔍
See Threats, Not Logs — AI Dashboards in QuickSight. Amazon QuickSight build visuals with NLPs, auto-refresh with SPICE, and go from nested JSON chaos to attack insights in minutes.
Introduction
AWS WAF logs every request evaluated, every action taken, every rule triggered, client fingerprints. geographic data and security labels. The problem? Most of the time, this goldmine sits in S3 as deeply nested JSON. Getting answers means either writing Athena queries from scratch every single time — or bleeding thousands per month piping it into a SIEM.
🔥 Sound Familiar?
It's 2 AM. An alert fires — latency spiking, request rate climbing. ⚠️
You scramble to Athena and start writing queries against your WAF logs. Or worse — you're downloading
.gz files from S3 and running gunzip | jq chains on your laptop like it's 2024. 💻Twenty minutes in, you're neck-deep in
CROSS JOIN UNNEST(httprequest.headers) syntax errors. 😤 You know requests are being blocked. But by who? What fingerprint? What endpoint are they targeting? Are they all using the same tool?✨ Now Imagine This Instead
You open a URL. One click and the dashboard shows in one view WAF traffic — pre-correlated, pre-filtered, ready to act on: No Athena. No syntax errors. No guessing. You write your mitigation rule in minutes, not an hour.
A QuickSight analysis connected to your WAF logs via Athena — set up once, then it just works.
Here's what you'll have when you're done:
🎯 Why This Works
🧠 AI-powered — Build visuals with NLP, Ask questions, get charts. No SQL needed in QuickSight.
📊 Easy-built visuals — IP, fingerprint correlation, label and geo breakdown — all in one place
🔄 Auto-refreshing — SPICE incremental refresh every 15 minutes
💰 Cost effective — SPICE stores data in-memory. Dashboard users query SPICE directly
🚫 No extra infrastructure — No Lambda, no Glue Crawler, no EventBridge
🔍 Interact with your data — Filter, drill down, explore patterns — everything in one dashboard
✅ What You Need First
- WAF logging enabled — Logs delivered to S3 via Kinesis Data Firehose
- Athena table — With partition projection. See AWS docs: Create WAF log table in Athena
- QuickSight Enterprise — With SPICE capacity available
🧹 Tame the Nested Beast
WAF logs are nested structs and arrays. QuickSight needs flat columns. Let's fix that. 🔧
Option A: Full history
1
2
3
4
5
6
7
8
9
10
11
12
13
14
CREATE OR REPLACE VIEW waf_logs_flat AS
SELECT
  from_unixtime(timestamp / 1000) AS request_time,
  action,
  httprequest.clientip AS client_ip,
  httprequest.country AS country,
  httprequest.uri AS uri,
  httprequest.httpmethod AS http_method,
  element_at(filter(httprequest.headers, x -\> lower(x.name) = 'host'), 1).value AS request_host,
  ja3fingerprint,
  ja4fingerprint,
  array_join(transform(labels, x -\> x.name), ' | ') AS all_labels,
  requestid AS request_id
FROM waf_logs;
Option B: Last 7 days (recommended — bounds SPICE size)
1
2
3
CREATE OR REPLACE VIEW waf_logs_flat_7d AS
SELECT * FROM waf_logs_flat
WHERE request_time \>= current_timestamp - interval '7' day;
🚀 From Zero to Dashboard
Step 1: Create Your Dataset in QuickSight
- QuickSight Console → Datasets → New dataset → Athena
- Select your flat view (
waf_logs_flatorwaf_logs_flat_7d) - Import to SPICE
- Note your Dataset ID:
1
2
3
4
aws quicksight list-data-sets \
  --aws-account-id $(aws sts get-caller-identity --query Account --output text) \
  --region us-east-1 \
  --query 'DataSetSummaries[?contains(Name,`waf`)].{Name:Name,Id:DataSetId}'
Step 2: Build Your Visuals
Create visuals using a
--definition JSON with the CLI. But honestly? Life's too short for JSON. 😅 Use QuickSight's Build (Q) AI feature with natural language prompts instead see next section. Example 1: Top Client IPs Table
1
2
3
4
5
6
7
8
9
10
11
12
13
14
15
16
17
18
19
20
21
22
23
24
25
26
27
28
29
30
31
32
{
  "TableVisual": {
    "VisualId": "top-client-ips",
    "Title": { "Visibility": "VISIBLE" },
    "ChartConfiguration": {
      "FieldWells": {
        "TableAggregatedFieldWells": {
          "GroupBy": [
            { "CategoricalDimensionField": {
                "FieldId": "client-ip-field",
                "Column": { "DataSetIdentifier": "waf_logs_flat", "ColumnName": "client_ip" }
            }},
            { "CategoricalDimensionField": {
                "FieldId": "country-field",
                "Column": { "DataSetIdentifier": "waf_logs_flat", "ColumnName": "country" }
            }}
          ],
          "Values": [
            { "CategoricalMeasureField": {
                "FieldId": "request-count",
                "Column": { "DataSetIdentifier": "waf_logs_flat", "ColumnName": "request_id" },
                "AggregationFunction": "DISTINCT_COUNT"
            }}
          ]
        }
      },
      "SortConfiguration": {
        "RowSort": [{ "FieldSort": { "FieldId": "request-count", "Direction": "DESC" }}]
      }
    }
  }
}
Example 2: Anti-DDoS Severity Donut Chart
1
2
3
4
5
6
7
8
9
10
11
12
13
14
15
16
17
18
19
20
21
22
{
  "PieChartVisual": {
    "VisualId": "anti-ddos-donut",
    "Title": { "Visibility": "VISIBLE" },
    "ChartConfiguration": {
      "FieldWells": {
        "PieChartAggregatedFieldWells": {
          "Category": [{ "CategoricalDimensionField": {
              "FieldId": "ddos-label-field",
              "Column": { "DataSetIdentifier": "waf_logs_flat", "ColumnName": "anti_ddos_label 1" }
          }}],
          "Values": [{ "CategoricalMeasureField": {
              "FieldId": "ddos-count",
              "Column": { "DataSetIdentifier": "waf_logs_flat", "ColumnName": "request_id" },
              "AggregationFunction": "DISTINCT_COUNT"
          }}]
        }
      },
      "DonutOptions": { "ArcOptions": { "ArcThickness": "MEDIUM" } }
    }
  }
}
Step 3: Import the Analysis
1
2
3
4
5
6
aws quicksight create-analysis \
  --aws-account-id "$ACCOUNT_ID" \
  --analysis-id "$(uuidgen | tr '[:upper:]' '[:lower:]')" \
  --name "WAF Security Dashboard" \
  --definition file://waf-dashboard-definition.json \
  --region us-east-1
Go grab a ☕. By the time you're back, open QuickSight → Analyses → "WAF Security Dashboard" — it's already there waiting for you.

🔮 Type What You Want. AI Builds It. That's It.
✨ QuickSight has a built-in AI assistant — Build (Q). Instead of writing JSON definitions, you describe what you want in plain English and it builds the visual for you.
Prompts in, charts out. Here are examples that generate the same visuals:

Top JA3 Fingerprints:
1
Top 50 ja3fingerprint by unique number of request_id sorted descending
Requests by Country:
1
Unique number of request_id by country
💬 That's it. No JSON. No field IDs. No syntax docs. Just tell it what you want to see — and it appears. Your security team just went from "let me write a query" to "let me ask a question." That's the shift. 🎤 ⬇️
🚀 Fuel Up: Docs That Actually Help
Enjoyed reading this content? Let the author know!
Your likes, comments, shares, and saves help creators reach more builders.

Loading recommendations
Loading article