
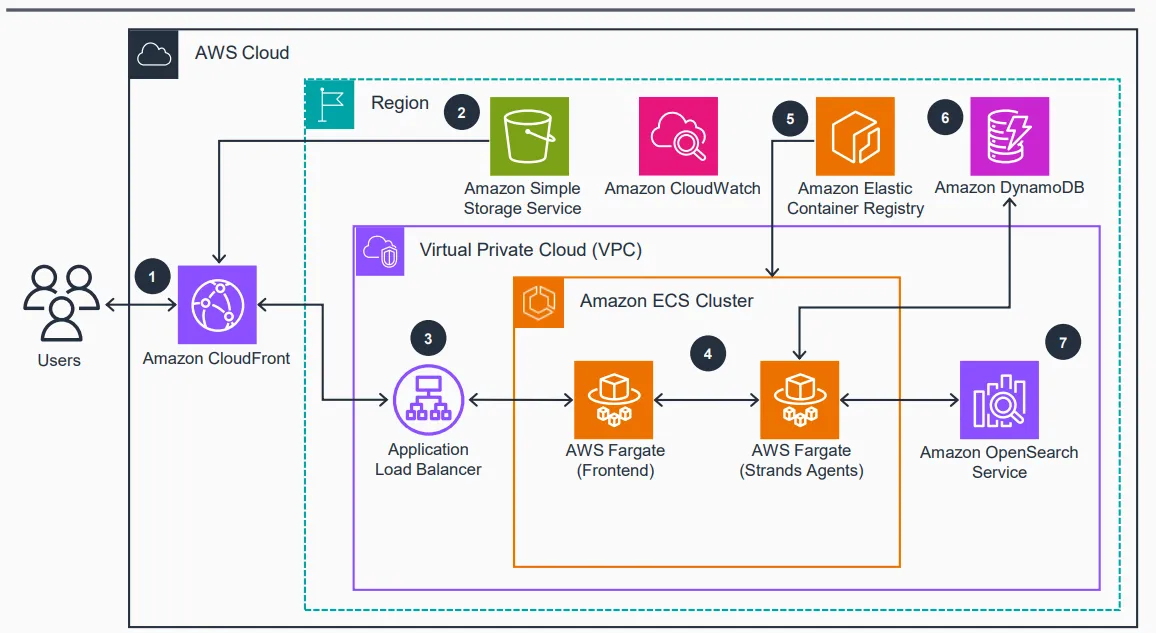
Your AI Agent Can Call an API. Should You Let It?
Everyone talks about what an AI agent can do. The more interesting question is what has to exist around the agent before you can actually trust it to do those things.
An AI model can generate an answer in a few seconds. An AI agent can do something with that answer.
That difference changes the engineering problem.
A traditional generative AI application can be represented fairly simply:
User → Prompt → Model → Answer
An agentic application introduces another layer of behavior:
User → Agent → Reason → Select a tool → Take an action → Observe the result → Continue or stop
The model is no longer only generating text. It can decide which tool to use, call an external system, receive the result, and use that result in the next step.
That is useful, but it also creates a problem that becomes increasingly important as agents move from demonstrations into real applications:
What infrastructure should exist between an AI agent and the systems it is allowed to control?
1. The chatbot was the easy part
A chatbot can usually operate inside a relatively simple boundary.
The model receives information, processes it and produces a response.
An agent has a larger responsibility.
For example, imagine an agent handling an order-management request:
User:
"Check my order and cancel it if it hasn't shipped."
"Check my order and cancel it if it hasn't shipped."
The agent may need to:
- Identify the customer's order.
- Check its current status.
- Determine whether cancellation is allowed.
- Call the cancellation API if appropriate.
- Confirm the result.
- Explain what happened to the user.
The important change is that the model is now participating in a workflow that can affect an external system.
The architecture therefore starts looking less like a chatbot and more like an application:
User
↓
↓
Agent
↓
Reasoning
↓
Tool selection
↓
Tool/API
↓
External system
↓
Result
↓
Agent
↓
Reasoning
↓
Tool selection
↓
Tool/API
↓
External system
↓
Result
↓
Agent
AWS's current agentic AI direction reflects this shift toward agents that can operate across tools and data while requiring security, identity, governance and monitoring around those actions.
2. What happens when an agent leaves the demo?
A prototype might only need:
LLM + prompt + tool
A production system needs considerably more.
The agent needs somewhere to run. It may need memory. It needs a controlled way to access tools. It needs identity and permissions. And once the system is running, developers need to know what the agent actually did.
This is where Amazon Bedrock AgentCore becomes interesting.
AgentCore is not simply another foundation model API. AWS describes it as a platform for building, deploying and operating agents, with modular services that can work together or independently. It is designed to work with different agent frameworks and foundation models rather than forcing everything into one model or framework.
A simplified view looks like this:
AI Agent
↓
Runtime
Memory | Gateway | Identity | Policy | Observability
↓
Models, tools, APIs and data
The interesting part is that these components solve different problems.
3. AgentCore isn't the "brain"
It is easy to look at an agent platform and think that the platform itself is the AI.
That is not the right way to think about it.
The foundation model provides the reasoning capability. AgentCore provides infrastructure around the agent so that the agent can operate as part of a larger application.
Runtime
The runtime is where the agent code runs.
Instead of treating the agent as something that only exists inside a notebook or local development environment, AgentCore Runtime provides a managed environment for deploying and scaling agent workloads.
Memory
An agent may need information beyond the current request.
Memory can provide context across interactions and help create more context-aware experiences.
This becomes particularly useful when an agent has to work through longer workflows rather than answering isolated questions.
Gateway
Agents become more useful when they can access tools.
AgentCore Gateway provides a controlled entry point for connecting agents with tools and services. AWS documents Gateway support for MCP, allowing agents to discover and invoke tools through a standardized protocol.
Identity
An agent that can access an API needs an identity.
AgentCore Identity is designed for authentication, authorization and credential management for AI agents and automated workloads.
Observability
An agent can make several decisions and tool calls during one request.
Simply knowing that the final answer was wrong isn't enough.
Developers need to understand what happened in between.
AgentCore Observability provides metrics, traces and logs through Amazon CloudWatch, including information such as sessions, latency, token usage and errors.
4. The tool problem
Tools are where agentic applications become particularly interesting.
Consider an agent with access to:
- a customer database
- an order API
- an email service
- a payment system
The agent might be able to decide which tool is appropriate for a request.
That creates a very different security model from a chatbot.
A poorly designed architecture could look like:
Agent
↓
↓
Broad API access
↓
Production systems
↓
Production systems
The model might be capable of choosing an action, but capability is not the same thing as authorization.
A safer architecture introduces boundaries:
Agent
↓
↓
Identity
↓
Policy / validation
↓
Tool gateway
↓
Authorized API
↓
Production system
↓
Policy / validation
↓
Tool gateway
↓
Authorized API
↓
Production system
This distinction matters because an agent can make mistakes.
A wrong chatbot response might simply require another question.
A wrong API call could modify a database, create an order, delete information or trigger an external process.
That is why identity, authorization, policies, guardrails and observability become architectural concerns rather than optional additions.
5. MCP changes the tool layer
Another important development in the agent ecosystem is the Model Context Protocol (MCP).
The basic idea is straightforward: instead of every AI application inventing its own way to discover and call tools, MCP provides a standardized protocol for connecting AI applications with tools and data.
AgentCore Gateway supports MCP and can expose tool capabilities to agents through the protocol. AWS documentation describes MCP as a standardized way for agents to discover and invoke tools through an AgentCore Gateway.
A simplified architecture looks like this:
AI Agent
↓
AgentCore Gateway
↓
MCP
↓
Tool 1 | Tool 2 | Tool 3
↓
**** APIs / Databases / Services
This separation is useful because the agent does not have to contain every integration directly.
The gateway can become the controlled boundary between the agent and the tools it can access.
AWS is already demonstrating this pattern in production-style architectures where AgentCore Gateway sits between agents and MCP-based tools.
6. Not every decision needs a giant LLM
There is another interesting direction emerging around agents: using smaller models for specific decisions instead of asking a large model to handle everything.
AWS has highlighted Strands Decider 2B, a smaller decision model designed for typed decisions such as tool selection, policy classification, guardrails, model routing and context selection.
Instead of generating a long response, the model can answer a narrower question such as:
"Which tool should the agent use?"
For example:
Agent
↓
Decision: Which tool?
↓
Decider
↓
Search API / Database / Calculator
The idea is not to replace larger models.
It is to avoid using a large general-purpose model for every small decision in an agent workflow.
That leads to a useful architectural question:
Does every step in an agent workflow actually require the same amount of intelligence?
For repetitive, well-defined decisions, the answer may be no.
AWS has also highlighted this approach in its recent AI-builder updates around Strands Decider 2B.
7. The cost problem
Agentic systems can perform multiple model calls during a single user interaction.
A request might look like:
User request
↓
LLM call
↓
Tool selection
↓
Tool call
↓
LLM call
↓
Another tool
↓
LLM call
↓
Final response
One request can therefore become several inference and tool operations.
That makes token usage, latency and execution efficiency important architectural considerations.
It also creates an interesting optimization problem:
How much intelligence should each step of an agent actually require?
A larger model may be appropriate for complex reasoning.
A smaller model, deterministic rule or policy engine may be enough for a simple classification or routing decision.
The goal is not simply to make the agent smarter.
It is to make the entire workflow appropriate for the task.
8. The security problem gets bigger when agents can act
A model that generates text is one thing.
A model that can act on behalf of a user is another.
Consider the difference:
Chatbot
"Your order appears eligible for cancellation."
Agent
Checks the order → validates the policy → calls the cancellation API → changes the order status.
The second system needs stronger controls because the model has become part of an operational workflow.
This introduces questions such as:
- Which identity is the agent using?
- Which resources can it access?
- Which tools can it call?
- Which actions require additional authorization?
- What happens if a tool receives unexpected arguments?
- How can an administrator investigate an action later?
- How can a session be stopped if something goes wrong?
AWS's AgentCore architecture addresses these concerns through separate capabilities for identity, policy, gateway and observability rather than treating the model itself as the security boundary.
This is an important shift in how agentic applications need to be designed.
The model should not be the final authority over what it is allowed to do.
9. Observability becomes part of the application
Traditional applications already need logs and metrics.
Agents add another layer: reasoning and tool execution can be non-linear.
An agent might:
- Receive a request.
- Select a tool.
- Call the tool.
- Receive an unexpected result.
- Change its plan.
- Call another tool.
- Produce a response.
If the final answer is wrong, developers need to investigate the path that led there.
AgentCore Observability provides visibility into agent execution through CloudWatch, including traces, metrics and logs. AWS documents metrics such as invocations, latency, resource utilization and error rates for AgentCore Runtime.
The architecture therefore becomes:
Agent
↓
Execute
↓
Observe
↓
Measure
↓
Improve
Observability isn't something added after deployment.
For an agent that can take actions, understanding its execution path is part of operating the system.
10. What AWS is really changing
The interesting change isn't simply that AWS has more AI models.
It is that the architecture around AI is changing.
The progression looks something like this:
Cloud infrastructure
↓
Managed services
↓
Serverless applications
↓
Generative AI applications
↓
AI agents
↓
Infrastructure for operating AI agents
The last step is where things get interesting.
An AI agent needs more than a model.
It needs a runtime.
It may need memory.
It needs tools.
It needs identity.
It needs policies.
It needs monitoring.
And it needs a controlled way to interact with the systems around it.
That is the problem platforms such as Amazon Bedrock AgentCore are trying to solve.
The next generation of cloud applications may not only contain software that responds to requests.
They may contain software entities that can decide, call tools, maintain context, interact with services and continue working through a task.
Once software can take actions, the infrastructure around that software becomes just as important as the model behind it.
And that may be the more important shift happening in cloud AI right now.
Enjoyed reading this content? Let the author know!
Your likes, comments, shares, and saves help creators reach more builders.

Loading recommendations
Loading article