
AWS Three-Tier Web Application Infrastructure with Terraform
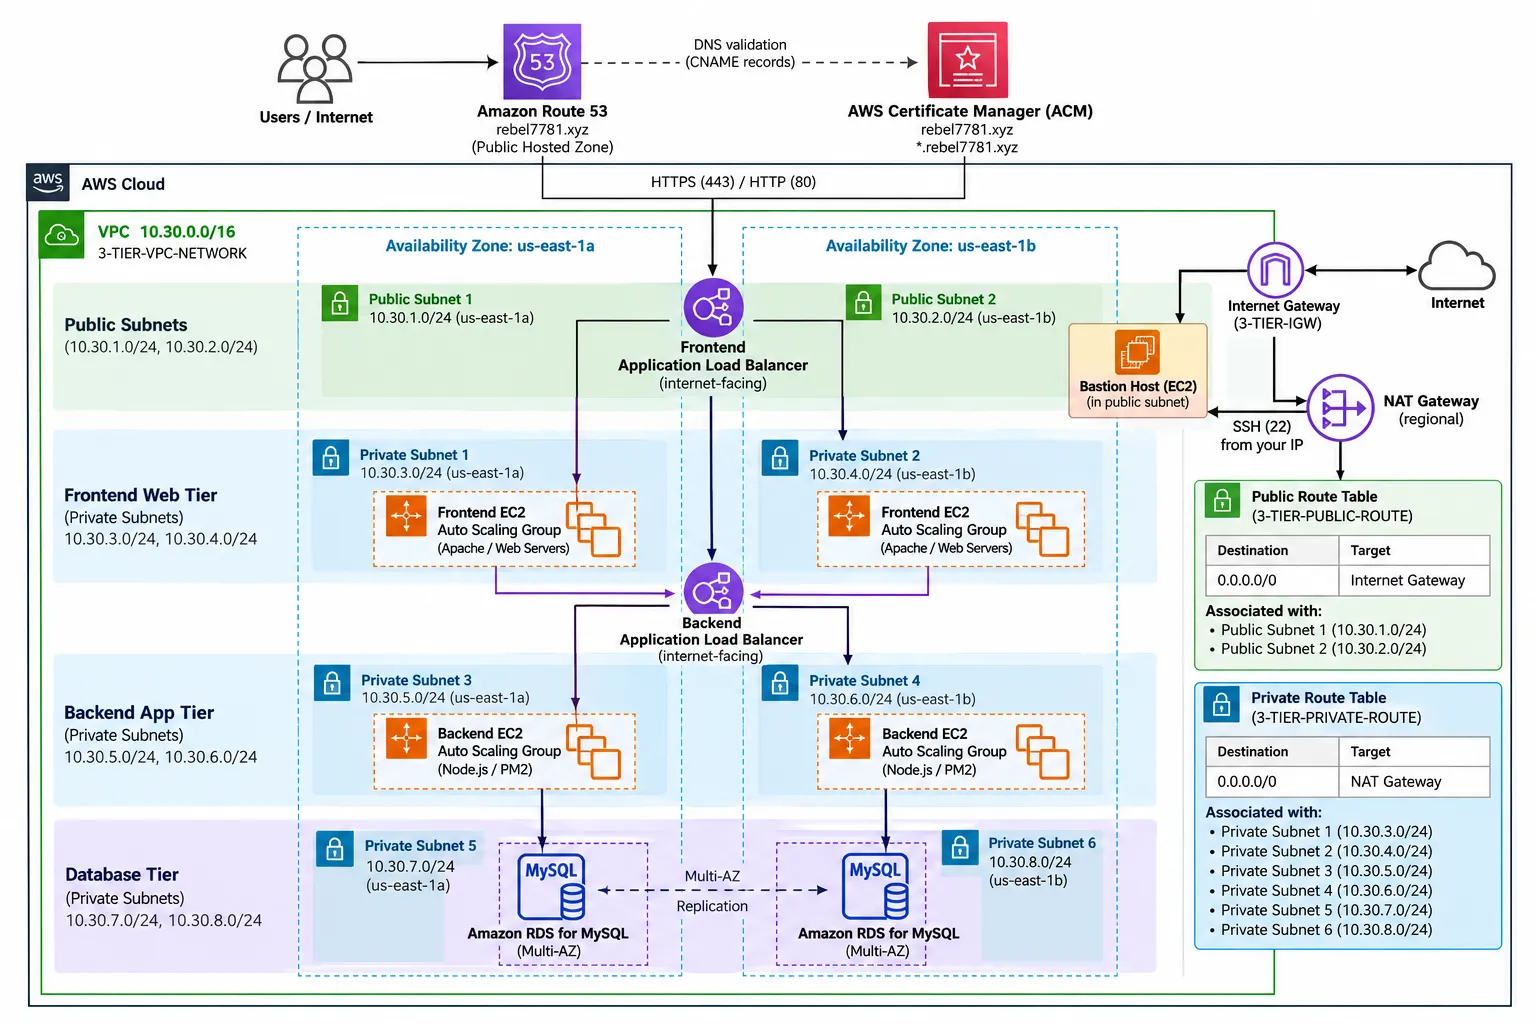
Architected and automated an enterprise Three-Tier Web App on AWS using modular Terraform. Spans a Multi-AZ VPC with isolated public/private subnets, Regional NAT Gateway, and dual ALBs with automated ACM TLS termination. Web (Apache) and App (Node.js/PM2) tiers scale across private subnets via EC2 Auto Scaling with zero public IPs. Persists data to an isolated Amazon RDS MySQL database using Route 53 private DNS discovery, secured by a bastion jump host and automated GitHub Actions CI/CD.
Built and automated a high-availability Three-Tier Web Application Infrastructure on AWS using modular Terraform(
v1.5+). The architecture decouples web, application, and database tiers across two Availability Zones (us-east-1a and us-east-1b) following AWS Well-Architected Framework principles.Key Architecture Highlights
- VPC & Network Segmentation: Custom VPC (
10.30.0.0/16) with 2 public subnets and 6 private subnets. Outbound internet for private instances routed securely via a Regional AWS NAT Gateway. - Application Delivery: Dual Application Load Balancers with HTTP (80) and HTTPS (443) listeners, secured with an automated wildcard SSL/TLS certificate from AWS Certificate Manager (ACM).
- Compute & Auto Scaling: Web (Apache) and Application (Node.js/PM2) tiers run in private subnets via EC2 Auto Scaling Groups with zero public IP addresses.
- Data Persistence: Amazon RDS MySQL deployed in an isolated database subnet group (
publicly_accessible = false) with internal discovery via a Route 53 Private Hosted Zone (book.rds.com). - Administrative Perimeter: Secure public-subnet Bastion Host for SSH tunneling.
Key Technical Challenges Solved
- Terraform DAG Dependency Cycle: Resolved a circular dependency between Route 53, ACM, and ALBs by querying the hosted zone via an independent data source.
- Automated ACM DNS Validation: Enforced
aws_acm_certificate_validationto eliminateUnsupportedCertificateerrors before ALB listener creation. - AWS ELB Constraints: Standardized resource naming to adhere to ELBv2 alphanumeric and hyphen requirements.
Skills Demonstrated & Links
- AWS Services: VPC, EC2, Auto Scaling, ALB, RDS, Route 53, ACM, NAT Gateway.
- DevOps Tools: Terraform Modules, GitHub Actions CI/CD, TFLint, Checkov.
- GitHub Repository: https://github.com/someshtarra/terraform-aws-three-tier-web-app
Enjoyed reading this content? Let the author know!
Your likes, comments, shares, and saves help creators reach more builders.

Loading recommendations
Loading article