
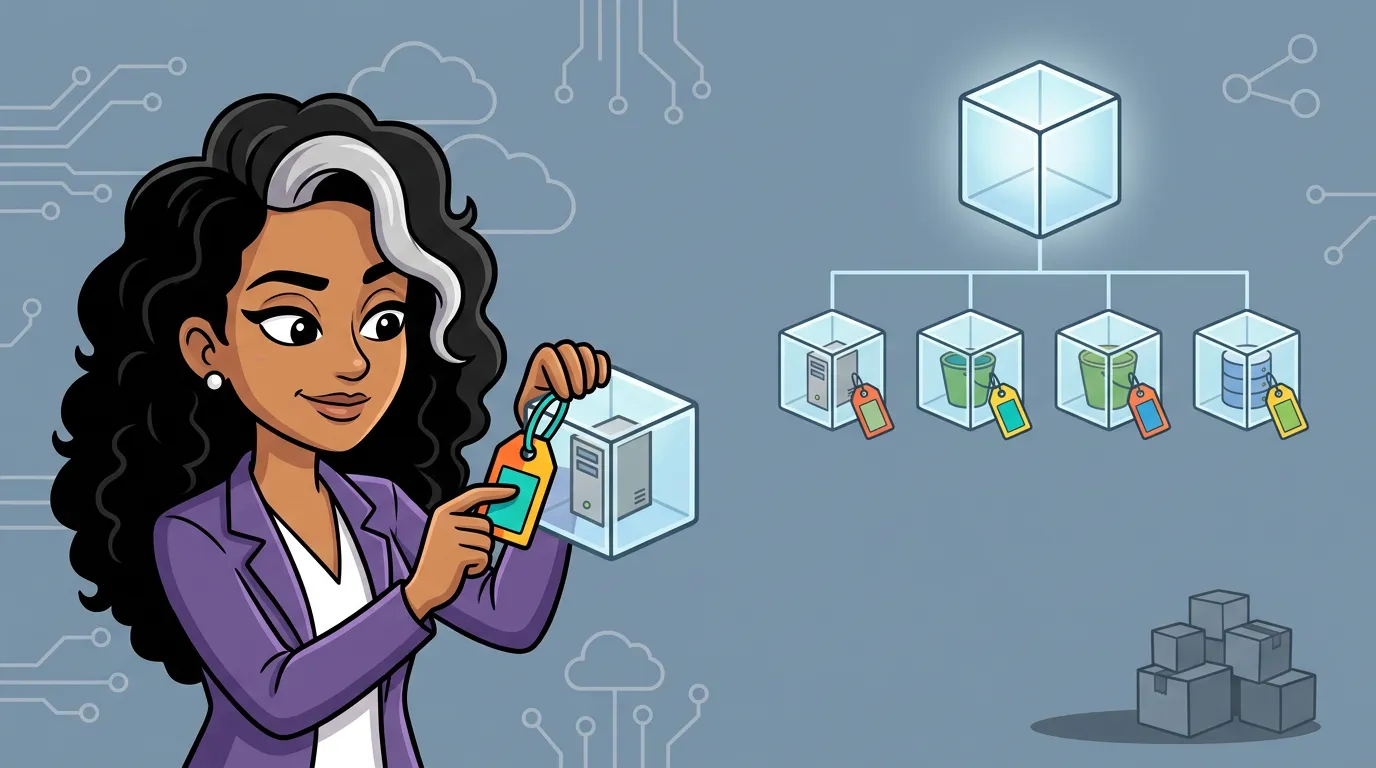
Cost Allocation Tags on AWS: Standalone Account vs. AWS Organizations
Why tag activation works differently in a standalone account and in an Organization, why Access Denied in a member account is expected, and the pitfalls that leave half your bill unallocated.
Tagging looks like the simplest topic in FinOps. You stick a label on a resource, it shows up in the report, and now you know how much each project, team or customer spends.
In theory.
In practice, cost allocation tags behave quite differently depending on where you are: in a standalone AWS account, or inside an AWS Organization with a management (payer) account and several member accounts. That second setup, very common in partner and customer scenarios, is exactly where the confusion starts: Access Denied messages, and reports with half the cost showing up as unallocated.
In this article I separate the two worlds: how tags work in a standalone account, what changes inside an Organization, and the pitfalls that apply to everyone.
First things first: a tag has two moments
There is one distinction that clears up most of the confusion. A cost allocation tag goes through two different moments, and they happen on different screens.
Applying the tag to the resource. This is attaching the label, such as
environment=production or cost-center=sales, to an EC2 instance, an S3 bucket, an RDS database. You can do this in the Tag Editor, through the API or, by far the best option, through infrastructure as code.Activating the tag key for cost allocation. Applying the label does not make costs show up split by it. You need to tell AWS that you want to use that key as a cost dimension, on the Cost Allocation Tags page in the Billing and Cost Management console. Only then does the key become a usable dimension in Cost Explorer and in the Cost and Usage Report.
Keep these two moments in mind. The gap between them is what changes once you enter an Organization.
Scenario 1: the standalone account
In a single account, without an Organization, life is simple. Both moments happen in the same account. You tag your resources, go to the Cost Allocation Tags page, activate the key, and shortly afterwards you can see costs split by it in Cost Explorer.
Everything lives in the same place. Whoever administers the account controls both applying and activating, and sees 100% of its own costs. There is no hierarchy and no debate about who owns what.
It is the most direct scenario. It is also the least common in enterprise environments, which is why most of the content available about tagging does not help the people who actually need it.
Scenario 2: AWS Organizations
This is the key point, and the one most articles skip. In an Organization, the two moments are split across different accounts, which creates a clear hierarchy.
Activation only exists in the management account
You can tag resources in any member account as usual. But activating a key for cost allocation can only be done in the management account. It is centralized and applies to the whole Organization.
The practical consequence: if you open the Cost Allocation Tags page inside a member account, you will see an Access Denied message stating that tags are managed at the management (payer) account level.
This scares a lot of people, and everyone starts tweaking IAM policies to fix it. It is not an error and it is not a missing permission. It is expected behavior. A member account does not manage cost allocation tags; it only consumes them. Not even
AdministratorAccess changes that, because the feature simply is not available there.Each member account only sees its own costs
Once the key is activated in the management account, each member account can see its own usage split by that tag. One account cannot see another account's costs.
Pay attention to this detail, because it is strategic: what isolates customers or teams in an Organization is not the tag. It is the fact that each account's cost view is scoped to itself. A tag is granularity, not a boundary.
The partner and customer perspective
This model maps neatly onto the partner and customer relationship.
The partner usually owns the management account. They activate the keys, define governance and see the consolidated view.
The customer usually operates in a member account. They tag their own resources and consume the cost view, but depend on the partner to activate the keys.
And for the customer to actually open Cost Explorer, two more settings are needed, both under the partner's control:
- Linked account access enabled in the Cost Management preferences of the management account, allowing member accounts to use Cost Explorer.
- IAM permissions for Cost Explorer and Billing on the user or role inside the customer's account.
Without these two, the key can be active and the customer still sees nothing, because they cannot even open the tool. This ticket gets opened a lot, and it is almost always misdiagnosed as a tagging problem.
Two features that only make sense in an Organization
Account-level cost allocation tags. You tag the account itself in AWS Organizations, and all costs of that account are attributed to that tag, including items a resource tag never reaches, such as credits, refunds and fees. For allocation by business unit, customer or division in a multi-account model, this is usually more robust than tagging resource by resource.
Tag policies. Rules in AWS Organizations that standardize keys and values across all accounts, avoiding the classic chaos of "cost center" spelled three different ways living side by side as if they were different things. And for Cost Explorer, they are.
Pitfalls that apply to both worlds
Whether you are in a standalone account or in an Organization, some behaviors catch almost everyone by surprise.
Tags are not retroactive. Costs are attributed to a tag from the date the key is activated, going forward. All prior history shows up as unallocated, unless you use the backfill option for cost allocation tags, which reapplies them to past usage (up to 12 months back).
Resources should be born tagged. Tagging later, in an environment already in production, works but has limits, especially for compute, and it does not fix history. Tagging through code, at creation time, is the practice that separates the teams that suffer from the ones that do not.
Not every tagged resource generates cost. An ECS task definition costs nothing; it is just the application blueprint. The cost comes from running tasks, which do not inherit tags automatically: you need to configure tag propagation. Tagging the wrong resource gives the false impression that tags do not work, when in fact no cost is attached to it.
Part of the bill will never be split by resource tags. Some data transfer, NAT Gateway processing, part of CloudWatch, Support plans, taxes, credits and refunds cannot be tagged at the resource level. This is where account tags and Cost Categories add value in an Organization, because they can allocate what resource tags cannot.
Analysis does not happen on the tags page. The Cost Allocation Tags page is only for activating keys. Analysis happens in Cost Explorer, grouping by tag. When you group, you will see two groups: resources that have the key, listed by value, and a "No tag key" bucket. That bucket is exactly your coverage gap, and it is the number worth tracking.
Tag or account as the cost boundary?
One last strategic point, which only shows up when you think in terms of an Organization.
The most reliable cost allocation on AWS is not the tag. It is the account itself. If each customer, team or environment has a dedicated account, that customer's cost is already isolated, without depending on any label.
AWS's own guidance combines both:
- Accounts as the boundary for the macro split: customer, business unit or environment.
- Tags for granularity within each account: project, application, owner.
- Cost Categories and account tags on top, to reconcile whatever is left.
Quick summary
In a standalone account, you apply and activate tags in the same place. Simple, no hierarchy.
In an Organization, applying is local and activating is centralized in the management account. Access Denied in a member account is normal, not a bug.
Each member account only sees its own costs, and that is what isolates customers and teams.
The partner governs and the customer consumes, but the customer still depends on linked account access and IAM permissions to see anything.
Tags are not retroactive, resources should be born tagged, and a slice of the bill will always remain untagged.
A good governance target: keep unallocated spend low, ideally under 5 to 10 percent, and cover the rest with account tags and Cost Categories.
Tags remain extremely important for cost allocation on AWS. But once you enter an Organization, they stop being a button you press on your own and become part of a governance model shared between whoever pays and whoever consumes. Understanding that split is what separates a trustworthy cost report from one full of unallocated spend.
References
Enjoyed reading this content? Let the author know!
Your likes, comments, shares, and saves help creators reach more builders.

Loading recommendations
Loading article