
AWS IAM: Why Permissions Matter
When I started learning AWS, one service that stood out to me was AWS Identity and Access Management (IAM).
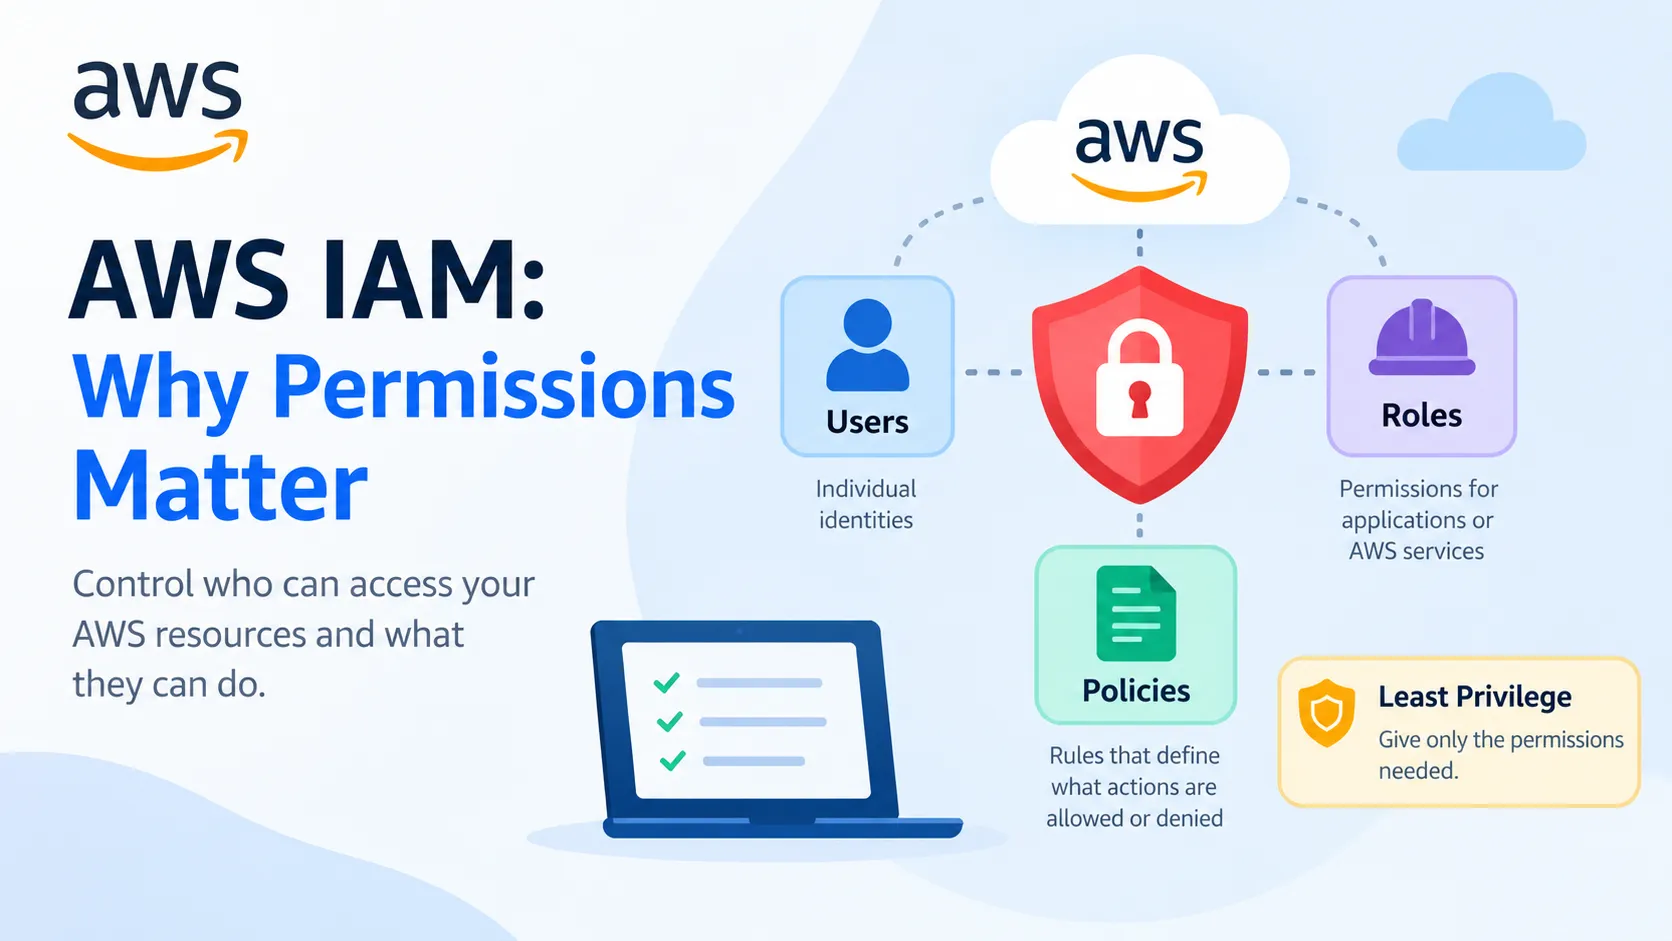
IAM controls who can access AWS resources and what they are allowed to do.
For example, an application may need permission to read files from an S3 bucket, while an administrator may need permission to create and manage AWS resources.
IAM mainly works with:
- Users – individual identities
- Roles – permissions that applications or AWS services can assume
- Policies – rules that define what actions are allowed or denied
One important concept I learned is least privilege: give users and applications only the permissions they actually need.
This helps reduce the risk of accidental or unauthorized access.
As I continue learning AWS, understanding IAM seems important because security is involved in almost every AWS service.
What AWS security concept did you find most important when you started learning AWS?
Enjoyed reading this content? Let the author know!
Your likes, comments, shares, and saves help creators reach more builders.

Loading recommendations
Loading article