
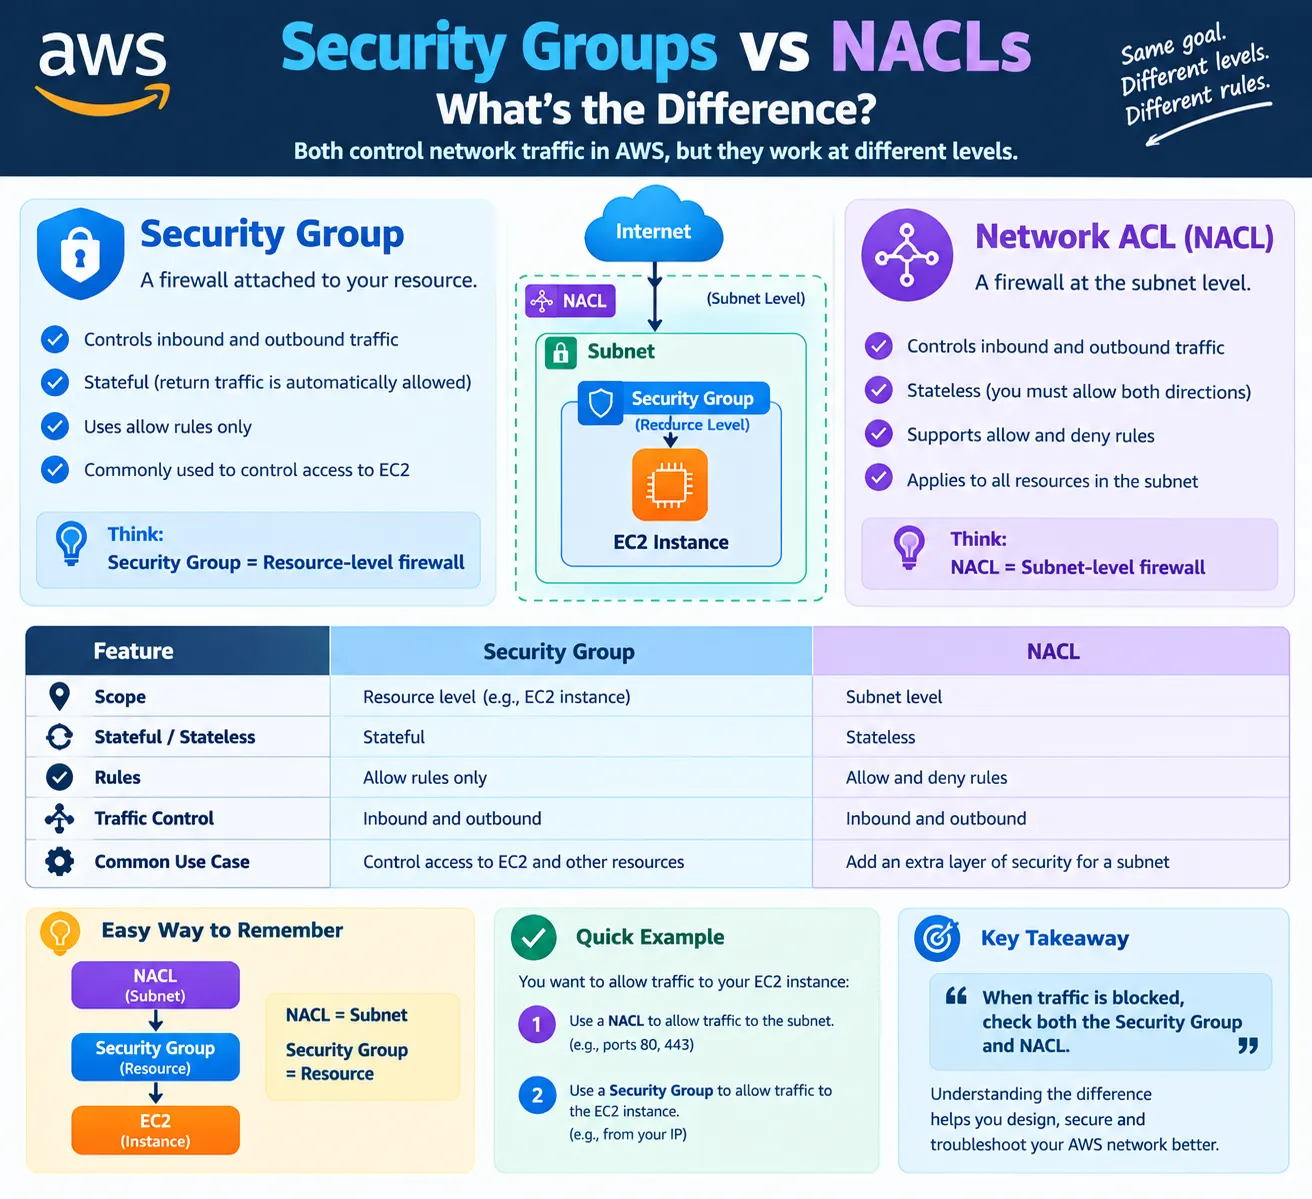
AWS Security Groups vs NACLs: What's the Difference?
Security Group or NACL? Both control network traffic, but they work at different levels.
Both Security Groups and Network ACLs (NACLs) control network traffic in AWS, but they work differently.
Security Group
Think of a Security Group as a firewall attached to your resource, such as an EC2 instance.
- Controls inbound and outbound traffic
- Stateful
- Uses allow rules
- Commonly used to control access to EC2
Think:
Security Group = Resource-level firewallNetwork ACL
A NACL works at the subnet level.
- Controls inbound and outbound traffic
- Stateless
- Supports allow and deny rules
- Applies to resources within the subnet
Think:
NACL = Subnet-level firewallEasy Way to Remember
1
2
3
4
5
6
7
NACL
 ↓
Subnet
 ↓
Security Group
 ↓
EC2
NACL = Subnet
Security Group = Resource
Understanding this difference makes AWS networking much easier to troubleshoot.
When traffic is blocked, check both the Security Group and NACL.
Enjoyed reading this content? Let the author know!
Your likes, comments, shares, and saves help creators reach more builders.

Loading recommendations
Loading article