
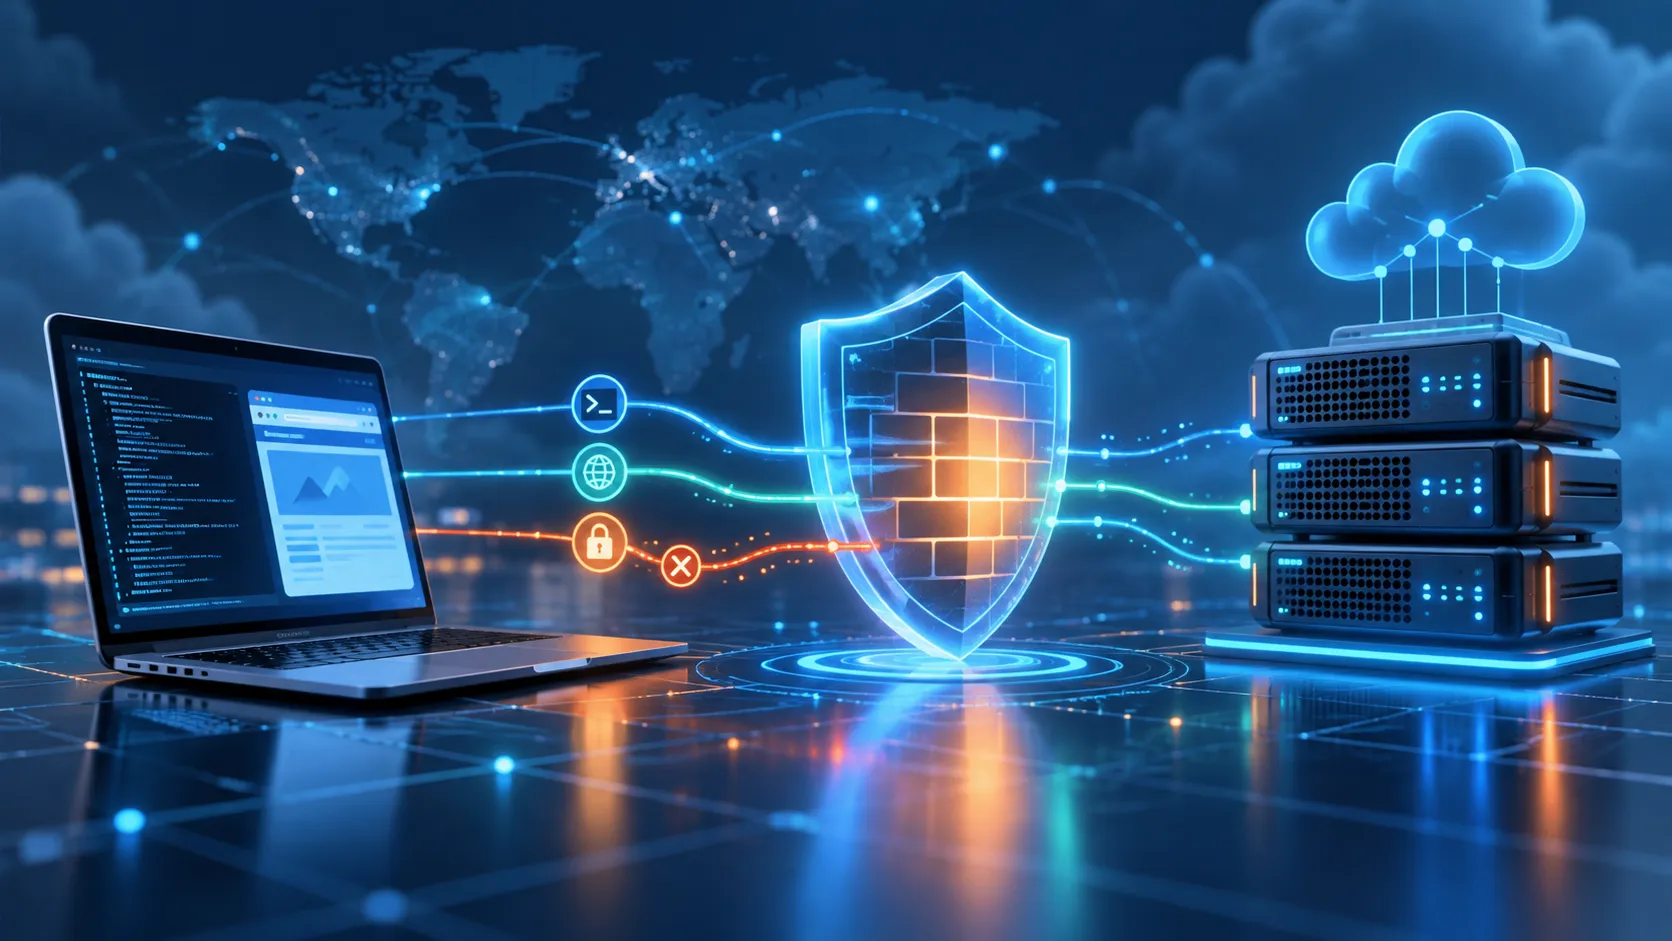
Understanding AWS Security Groups: How SSH and Web Access Really Work
A beginner-friendly explanation of AWS Security Groups, inbound and outbound rules, and how ports like 22, 80, and 443 control access to EC2 instances.
Understanding AWS Security Groups: How SSH and Web Access Really Work
When I first started working with Amazon EC2, one of the most important concepts I had to understand was the Security Group.
Launching an EC2 instance is only part of the process. Even if the instance is running correctly, you may still be unable to connect to it unless the network access rules are configured properly.
This article explains AWS Security Groups in a simple way.
What is a Security Group?
A Security Group acts as a virtual firewall for AWS resources such as EC2 instances.
It controls what network traffic is allowed to enter and leave a resource.
Security Groups mainly contain two types of rules:
- Inbound rules
- Outbound rules
Inbound Rules
Inbound rules control traffic coming into the EC2 instance.
For example, if you want to connect to an Amazon Linux server using SSH, the instance must allow traffic on:
1
2
3
Port: 22
Protocol: TCP
Service: SSH
If port 22 is not allowed, your SSH connection will fail even if the server itself is running.
Outbound Rules
Outbound rules control traffic leaving the EC2 instance.
For many beginner setups, the default outbound rule allows the instance to communicate with external services.
This is useful when the EC2 instance needs to:
- Download software packages
- Access APIs
- Connect to databases
- Reach external websites
Understanding Common Ports
Different services use different network ports.
Some common examples are:
1
2
3
SSH   → Port 22
HTTP  → Port 80
HTTPS → Port 443
If you are running a website on an EC2 instance, the required web ports must be allowed in the Security Group.
Example: SSH Connection
Suppose you launch an Amazon Linux EC2 instance.
You want to connect using:
1
ssh -i my-key.pem ec2-user@PUBLIC_IP
The connection flow is roughly:
1
2
3
4
5
6
7
8
9
10
11
12
13
Your Computer
      |
      | SSH Request
      | Port 22
      v
Internet
      |
      v
AWS Security Group
      |
      | Is Port 22 allowed?
      v
EC2 Instance
If the rule allows your connection, the request reaches the EC2 instance.
If the rule blocks the connection, SSH will fail.
Source IP Matters
Security Group rules can also restrict traffic based on the source IP address.
For example, SSH access can be configured to allow only your own IP address.
This is safer than allowing SSH access from everywhere.
A broad rule such as:
1
0.0.0.0/0
means traffic can come from any IPv4 address.
This may be suitable in some cases for public web traffic on ports 80 or 443, but using it for administrative ports such as SSH should be avoided unless there is a specific reason.
Security Groups are Stateful
An important characteristic of AWS Security Groups is that they are stateful.
If an inbound connection is allowed, the response traffic is automatically allowed back.
You do not need to manually create a separate rule for the return traffic.
This simplifies network configuration.
Security Group vs Firewall
A traditional firewall and an AWS Security Group perform similar roles, but Security Groups are managed directly inside AWS.
They are attached to cloud resources and can be updated without modifying the operating system firewall.
This creates multiple layers of protection.
For example:
1
2
3
4
5
6
7
8
9
10
Internet
   |
   v
AWS Security Group
   |
   v
Operating System Firewall
   |
   v
Application
Common Beginner Mistake
One of the most common issues is:
“My EC2 instance is running, but I cannot connect to it.”
Possible reasons include:
- Port 22 is not allowed
- Wrong source IP is configured
- Incorrect public IP address
- Instance has no public network access
- The wrong key pair is being used
Understanding Security Groups makes troubleshooting much easier.
Example Web Server Rules
For a simple public web server, you may have:
1
2
3
4
5
6
7
8
9
10
11
SSH
Port: 22
Source: My IP

HTTP
Port: 80
Source: Anywhere

HTTPS
Port: 443
Source: Anywhere
This allows users to access the website while keeping SSH access more restricted.
Security Best Practices
When configuring Security Groups:
- Open only the ports you actually need
- Restrict administrative access where possible
- Avoid exposing unnecessary services
- Remove unused rules
- Review Security Groups periodically
A simple rule to remember is:
1
2
Allow only what is required.
Block everything else.
What I Learned
Security Groups helped me understand that cloud security is not only about usernames and passwords.
Network access itself must also be controlled.
A secure cloud setup depends on multiple layers:
1
2
3
4
5
6
7
Identity
+
Network Rules
+
Operating System Security
+
Application Security
Each layer plays an important role.
Conclusion
AWS Security Groups are one of the fundamental building blocks of cloud networking.
Once you understand ports, protocols, inbound rules, outbound rules, and source IP addresses, connecting to and securing EC2 instances becomes much easier.
Learning these concepts early also helps when moving toward more advanced AWS topics such as load balancers, VPC networking, private subnets, databases, and multi-tier architectures.
Enjoyed reading this content? Let the author know!
Your likes, comments, shares, and saves help creators reach more builders.

Loading recommendations
Loading article