
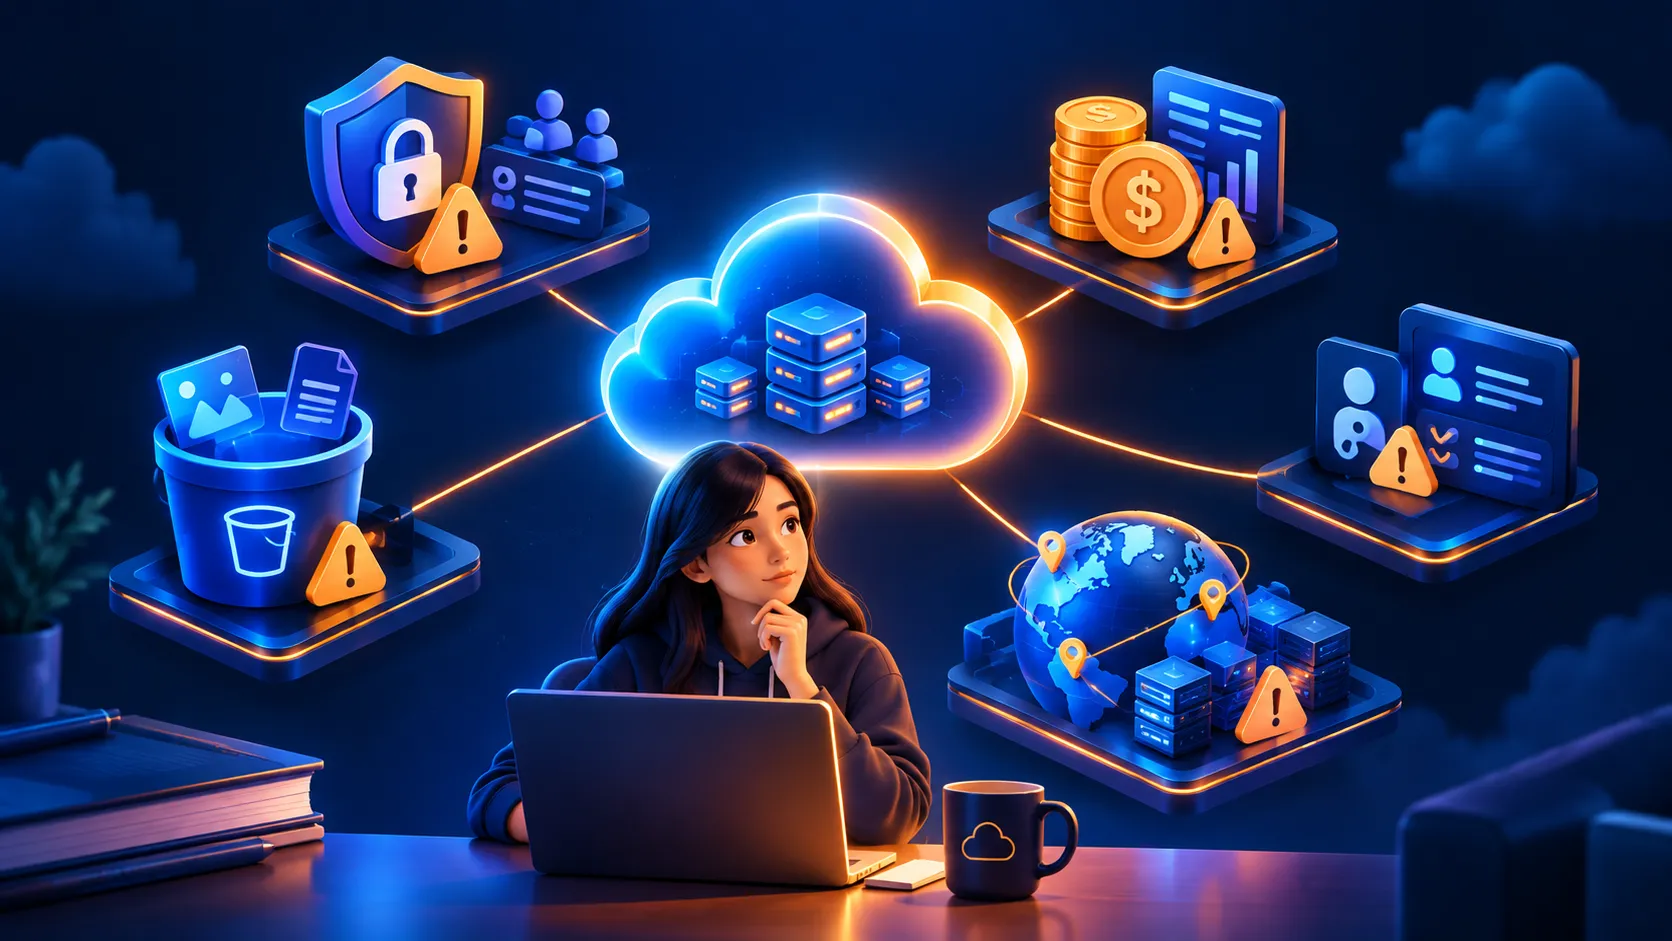
5 AWS Mistakes Beginners Make (And How to Avoid Them)
Starting your AWS journey? Here are 5 common mistakes beginners make with IAM, costs, security, and cloud architecture - explained simply so you can avoid them from day one.
Starting your AWS journey can feel overwhelming. With hundreds of cloud services, complex billing tiers, and strict security configurations, it is easy for newcomers to get lost.
The good news? You do not need to master every service on day one. Avoiding just a few common architectural and security missteps can save you significant time, money, and frustration.
Here are 5 critical AWS mistakes beginners make and practical habits to avoid them.
1. Granting Overly Permissive Access
One of the first tools every newcomer encounters is AWS IAM (Identity and Access Management). When troubleshooting permission errors, it is tempting to attach
AdministratorAccess to quickly unblock a project.However, violating security guardrails creates severe risks. Always apply the Principle of Least Privilege: grant only the minimum permissions necessary for an identity or service to do its job.
- Developers: Restrict permissions strictly to development environments.
- Storage Users: Grant access only to designated Amazon S3 buckets.
- Service Roles: Use temporary IAM Roles for EC2 instances or Lambda functions rather than hardcoded long-term access keys.
2. Overlooking Resource Costs and Idle Infrastructure
Cloud infrastructure can be provisioned in seconds, but forgetting to terminate temporary resources can lead to unexpected billing surprises.
A frequent beginner pattern is launching experimental instances or databases and leaving them active long after testing is finished.
Key Habits for Cost Control:
- Before deploying, verify whether the service qualifies under the AWS Free Tier.
- Set up AWS Budgets with email alerts to notify you before exceeding monthly spend thresholds.
- After concluding work, audit your dashboard and delete or stop idle resources immediately.
3. Treating Amazon S3 Like a Simple Shared Folder
While Amazon S3 provides object storage, it operates differently from standard local directories. Security depends entirely on explicit access policies.
Common configuration pitfalls include:
- Disabling Block Public Access settings without understanding the exposure risk.
- Forgetting to verify bucket policies, Object Ownership, and Access Control Lists (ACLs).
- Neglecting default server-side encryption settings.
Always prioritize security over convenience: verify who needs access before making any bucket or prefix accessible.
4. Viewing AWS as a Single Monolithic Data Center
AWS is built upon a globally distributed architecture composed of Regions and Availability Zones (AZs), alongside edge locations.
- AWS Region: A distinct physical geographic area across the globe.
- Availability Zone (AZ): One or more discrete data centers with redundant power, networking, and connectivity within an AWS Region.
Designing applications across multiple Availability Zones provides fault tolerance and high availability. Understanding this physical distribution is also a fundamental pillar of the AWS Certified Cloud Practitioner (CLF-C02) curriculum.
5. Assuming AWS Manages All Cloud Security
Under the AWS Shared Responsibility Model, security duties are divided between AWS and the customer:
- AWS (Security OF the Cloud): Physical data center facilities, hardware maintenance, virtualization hypervisors, and core networking.
- Customer (Security IN the Cloud): Customer data encryption, IAM credential governance, operating system patches on compute instances (e.g., Amazon EC2), and firewall configurations (Security Groups / Network ACLs).
AWS protects the underlying infrastructure; securing the applications and configurations placed inside remains the customer's duty.
Quick Comparison: Beginner Mistake vs. Best Practice
| Common Beginner Mistake | Recommended AWS Best Practice |
|---|---|
| Using full admin access everywhere | Apply Least Privilege and scoped IAM policies |
| Leaving test environments running indefinitely | Configure AWS Budgets and clean up idle resources |
| Making S3 buckets public for easy access | Keep S3 Block Public Access enabled by default |
| Deploying single-point-of-failure setups | Design across multiple Availability Zones (AZs) |
| Assuming AWS handles OS and data security | Follow the Shared Responsibility Model guidelines |
The 5-Point Builder Checklist
Before ending your cloud work session, run through this quick audit:
- Security: Are access permissions scoped strictly to what is required?
- Cost: Are there active instances accumulating unnecessary hourly charges?
- Storage: Are storage buckets encrypted and protected from public view?
- Availability: Is critical architecture resilient against single-zone failures?
- Hygiene: Have all temporary test stacks and unattached volumes been terminated?
Let's Discuss!
- Which AWS service or concept tripped you up the most when you were getting started?
- What is the #1 tip you would share with someone launching their very first EC2 instance?
Drop your experience in the comments below! If this guide helped clarify core AWS foundations, please consider leaving an Upvote to support the series.
Enjoyed reading this content? Let the author know!
Your likes, comments, shares, and saves help creators reach more builders.

Loading recommendations
Loading article