
Multi-Cloud Networking in Action: AWS Direct Connect Meets GCP Partner Interconnect
Multi-Cloud Networking in Action: AWS Direct Connect Meets GCP Partner Interconnect
In today's cloud-native world, organizations are increasingly adopting multi-cloud strategies to leverage the strengths of different cloud providers. One of the biggest challenges in a multi-cloud environment is establishing secure, reliable, and low-latency connectivity between workloads hosted across clouds.
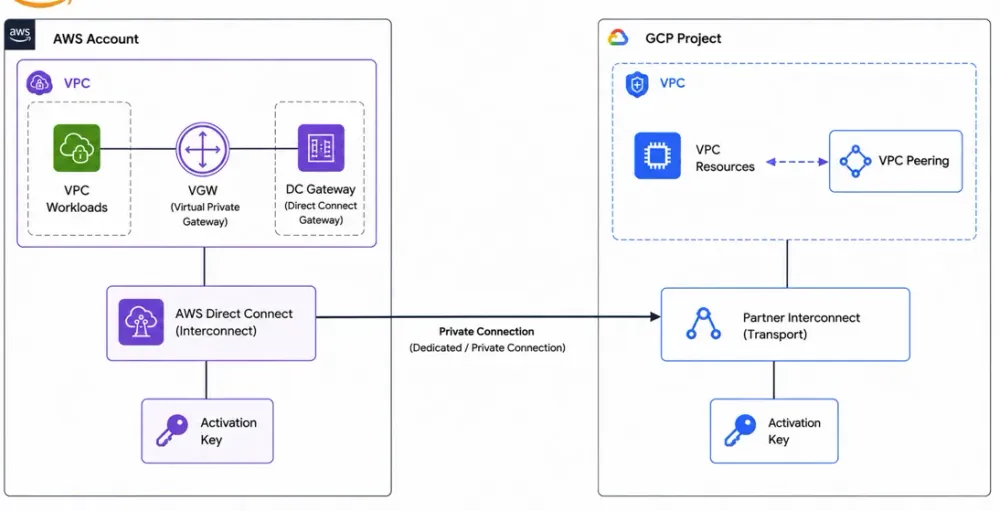
Recently, I worked on designing an architecture that enables private communication between Amazon Web Services (AWS) and Google Cloud Platform (GCP) using AWS Direct Connect and GCP Partner Interconnect.
Architecture Overview
The solution establishes a dedicated private network path between AWS and GCP without exposing traffic to the public internet.
AWS Components
- Amazon VPC hosting workloads
- Virtual Private Gateway (VGW)
- Direct Connect Gateway (DXGW)
- AWS Direct Connect
- Interconnect Activation Key
GCP Components
- GCP VPC hosting resources
- Partner Interconnect (Transport VPC)
- VPC Peering between Transport VPC and Application VPC
- Interconnect Activation Key
Why Use AWS Direct Connect and GCP Partner Interconnect?
Traditional VPN-based connectivity often relies on the public internet, which can introduce:
- Higher latency
- Variable performance
- Potential security concerns
- Bandwidth limitations
Using dedicated interconnects provides a more enterprise-grade solution by offering:
1. Private Connectivity
Traffic never traverses the public internet, significantly improving security and compliance.
2. Predictable Performance
Dedicated network paths ensure consistent throughput and reduced latency.
3. Scalability
The architecture can scale to support large data transfers and growing workloads.
4. Reliability
Enterprise-grade connectivity with high availability options.
Key Design Considerations
AWS Side
The Virtual Private Gateway (VGW) acts as the entry point for VPC routes, while the Direct Connect Gateway (DXGW) provides connectivity between AWS Direct Connect and the VPC.
Benefits include:
- Centralized connectivity management
- Support for multiple VPCs
- Flexible routing options
GCP Side
The Partner Interconnect terminates within a dedicated Transport VPC. Through VPC Peering, routes are extended to the application VPC hosting workloads.
Benefits include:
- Separation of networking and application resources
- Simplified architecture management
- Enhanced scalability
Security Benefits
This architecture strengthens security by:
i) Eliminating public internet exposure
ii) Reducing attack surfaces
iii) Supporting private IP communication
iv) Enabling compliance-focused networking
v) Providing controlled route propagation
Business Benefits
Organizations adopting this architecture can achieve:
- Faster application communication across clouds
- Improved user experience
- Better disaster recovery capabilities
- Hybrid and multi-cloud flexibility
- Reduced operational complexity
Enjoyed reading this content? Let the author know!
Your likes, comments, shares, and saves help creators reach more builders.

Loading recommendations
Loading article