
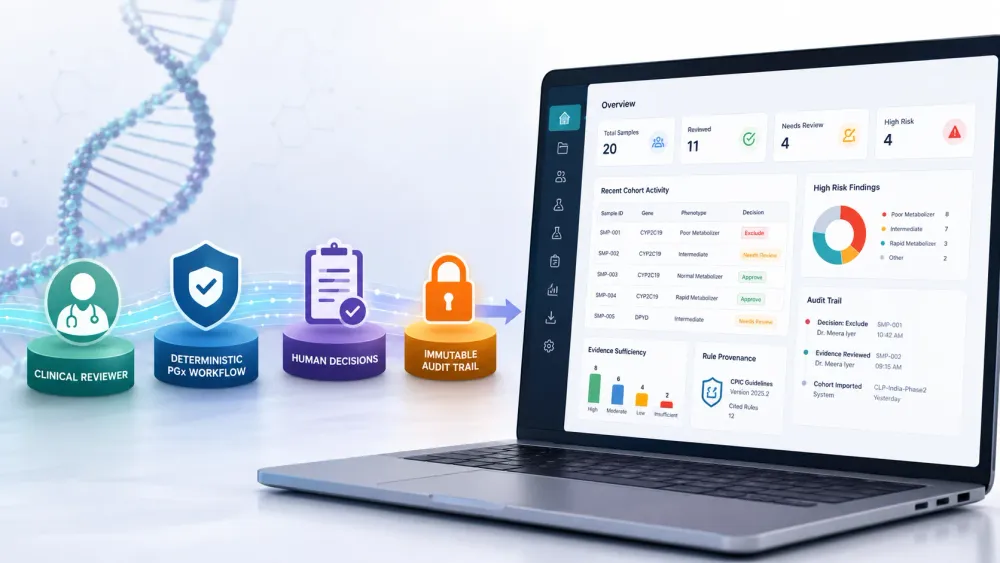
Building Anukriti EvidenceOps: A Pharmacogenomics Compliance Dashboard with Amazon DynamoDB and Vercel
How I built a clinical pharmacogenomics review and audit platform using Next.js 16, Vercel, and Amazon DynamoDB. The project focuses on deterministic PGx workflows, immutable audit trails, and audit-ready exports for biotech and CRO teams.
This article was created as part of my submission to the H0: Hack the Zero Stack with Vercel v0 and AWS Databases Hackathon. #H0Hackathon
Introduction
Pharmacogenomics (PGx) helps researchers understand how genetic variation affects drug response. While deterministic PGx engines can generate clinically relevant recommendations, there is still a major operational challenge:
How do biotech and CRO teams review, audit, approve, and operationalize those results at scale?
Most workflows today rely on spreadsheets, emails, PDFs, and fragmented documentation. Reviewer decisions are difficult to trace, audit histories are scattered, and exporting study-ready evidence packages often becomes a manual process.
To address this problem, I built Anukriti EvidenceOps, a governance and review platform for pharmacogenomics programs powered by Amazon DynamoDB and Vercel.
What Anukriti EvidenceOps Does
Anukriti EvidenceOps is designed for translational medicine teams, clinical researchers, and CRO reviewers.
The platform allows users to:
- Import pharmacogenomics cohort results
- Review deterministic PGx calls
- Examine evidence sufficiency and rule provenance
- Record reviewer decisions
- Maintain immutable audit trails
- Generate audit-ready exports
- Track compliance activity across studies
A core principle of the system is:
No LLM-generated medical decisions.
Every recommendation displayed in the application originates from deterministic pharmacogenomic rules and reviewer actions, making the workflow transparent, reproducible, and auditable.
System Architecture

The application is built as a full-stack Next.js platform deployed on Vercel with Amazon DynamoDB serving as the primary operational datastore.
Frontend
- Next.js 16 App Router
- React 19
- TypeScript
- Tailwind CSS
- shadcn/ui
AWS Services
- Amazon DynamoDB
- AWS IAM
- AWS SDK for JavaScript v3
Future export workflows are designed to extend into:
- DynamoDB Streams
- Amazon EventBridge
- AWS Lambda
- Amazon S3
Why I Chose DynamoDB
The data model is heavily driven by access patterns.
The application needs to support queries such as:
- List projects
- Retrieve cohort samples
- Fetch evidence reviews
- Display decision queues
- Show audit history
- Generate compliance exports
Rather than creating separate tables for every entity, I used a single-table DynamoDB design.
This approach keeps related data together while allowing efficient queries using carefully designed partition keys, sort keys, and secondary indexes.
EvidenceOps Table
| Entity | PK | SK |
|---|---|---|
| Project | PROJECT#id | META |
| Cohort | PROJECT#id | COHORT#cohortId |
| Sample | COHORT#id | SAMPLE#sampleId |
| PGx Run | SAMPLE#id | RUN#latest |
| Rule | RULE#id | META |
| Audit Event | AUDIT#entityId | EVENT#timestamp#id |
This structure allows most application screens to be backed by a single Query or GetItem operation.
Using Global Secondary Indexes
Two Global Secondary Indexes power the application's secondary access patterns.
GSI1
Used for:
- Decision queues
- Entity listings
- Global audit feed
Examples:
1
2
3
DECISION#approved
DECISION#needs-review
DECISION#excluded
This allows reviewers to instantly view samples requiring attention.
GSI2
Used for:
1
Sample-by-ID lookup
This supports direct navigation and sample retrieval regardless of cohort hierarchy.
Reviewer Decisions as DynamoDB Updates
One of the most important workflows in the application is recording reviewer decisions.
When a reviewer marks a sample as:
- Approved
- Needs Review
- Excluded
- Follow-Up Required
The system performs an UpdateItem operation that:
- Updates the decision state
- Records reviewer metadata
- Increments the review version
- Re-indexes the sample into the correct decision queue
This makes decision queues self-maintaining without requiring additional infrastructure.
Building an Immutable Audit Trail
Healthcare workflows require traceability.
Rather than modifying existing audit entries, every action generates a new append-only event.
Examples include:
- reviewer.decision.changed
- cohort.imported
- audit.pack.generated
- note.added
Every event is inserted with a conditional write using:
1
attribute_not_exists(PK)
This ensures that audit history cannot be accidentally overwritten.
The result is a tamper-resistant compliance trail that can be reviewed later by sponsors, reviewers, or regulatory stakeholders.
Next.js and DynamoDB Integration
One of the most enjoyable aspects of this project was how naturally Next.js App Router and DynamoDB fit together.
Server Components
Server Components fetch data directly from DynamoDB during rendering.
Examples:
- Dashboard
- Projects
- Cohorts
- Samples
- Rule Provenance
- Audit Trail
These routes are dynamically rendered on each request.
Server Actions
Server Actions handle mutations such as:
- Recording reviewer decisions
- Adding notes
- Generating audit packs
- Updating workflow state
This keeps database access entirely on the server and avoids exposing AWS logic to the client.
Security Model
The deployment uses a dedicated IAM policy that follows the principle of least privilege.
The application is restricted to:
- GetItem
- Query
- PutItem
- UpdateItem
against the EvidenceOps table and its indexes.
The application cannot:
- Create tables
- Delete tables
- Modify unrelated AWS resources
This provides a much safer deployment model for a public-facing application.
The User Experience
The application is intentionally designed as a healthcare operations platform rather than a consumer health product.
Key areas include:
Dashboard
- Active projects
- Samples reviewed
- High-risk findings
- Pending evidence review
Cohort Review
Reviewers can examine:
- Gene
- Diplotype
- Phenotype
- Evidence level
- Decision state
- Reviewer assignments
Evidence Review Drawer
The core review experience includes:
- Deterministic PGx Call
- Evidence Sufficiency
- Rule Provenance
- Population Context
- Reviewer Decision
- Audit History
Audit Pack Builder
Users can generate export packages containing:
- Cohort summaries
- Reviewer notes
- High-risk findings
- Rule provenance
- Export manifests
Challenges
The biggest challenge was designing a workflow that felt realistic for clinical research teams.
Building tables and dashboards is easy.
Designing a system that accurately represents reviewer workflows, audit requirements, evidence traceability, and pharmacogenomic governance is much harder.
Another challenge was translating those workflows into a scalable DynamoDB access model without sacrificing performance or simplicity.
Key Takeaways
A few lessons stood out during development:
- DynamoDB single-table design becomes extremely powerful when modeled around access patterns.
- Global Secondary Indexes can naturally support workflow queues.
- Conditional writes make immutable audit trails straightforward to implement.
- Next.js Server Components and Server Actions pair exceptionally well with DynamoDB.
- Governance and auditability are just as important as analytics in healthcare software.
What's Next
The next evolution of Anukriti EvidenceOps includes:
- Multi-reviewer approval workflows
- Electronic signatures
- DynamoDB Streams-based event processing
- EventBridge automation
- Lambda-powered export generation
- Amazon S3 audit-pack storage
- Sponsor collaboration portals
- Real-time compliance monitoring
Ultimately, the goal is to build a platform that helps pharmacogenomics programs become more transparent, reproducible, and operationally scalable.
Conclusion
Anukriti EvidenceOps demonstrates how Amazon DynamoDB and Vercel can be combined to build a production-style healthcare operations platform with minimal infrastructure overhead.
By combining deterministic pharmacogenomics workflows, immutable audit trails, and reviewer-driven governance, the platform creates a foundation for trustworthy and scalable pharmacogenomics operations.
Tech Stack: Next.js 16, React 19, TypeScript, Tailwind CSS, Amazon DynamoDB, AWS SDK for JavaScript v3, AWS IAM, Vercel
Built for the H0: Hack the Zero Stack with Vercel v0 and AWS Databases Hackathon.
#H0Hackathon
#H0Hackathon
Enjoyed reading this content? Let the author know!
Your likes, comments, shares, and saves help creators reach more builders.

Loading recommendations
Loading article