
eks 1.33 upgrade notes (for self managed nodes , moving from al2 to al2023)
aws is only releasing al2023 AMIs for eks 1.33 , this is intoducing some breaking changes as it no longer has the bootstrap script and has moved to using nodeadm
key points :
- aws is not releasing al2 AMIs for eks 1.33 , so if you are running self managed nodes you will have to switch to al2023 when upgrading your nodes
- the al2023 AMIs don't have the old bootstrap script (previously located at /etc/eks/bootstrap.sh) , instead switching to nodeadm , so if you think that you'll just switch the ami and keep the user data script , i have bad news for you , as your nodes won't join the cluster
- instead of running the script with variables , you will define a MIME file (think of it as a more complicated yaml of a configmap ) and put it in the user data of your launch template
- check the default template , reference , and playground .
now , let's compare an old bootstrap script with the new MIME file
1
2
3
4
5
6
7
8
#!/bin/bash
set -e
export CONTAINER_RUNTIME="containerd"
export USE_MAX_PODS=false
B64_CLUSTER_CA=<certificate authority>
API_SERVER_URL=<API server endpoint>
/etc/eks/bootstrap.sh <cluster name> --kubelet-extra-args '--max-pods=100 --node-labels group=<group name> --register-with-taints special-nodegroup=<group name>:NoSchedule' --b64-cluster-ca $B64_CLUSTER_CA --apiserver-endpoint $API_SERVER_URL \
  --ip-family ipv4 --service-ipv4-cidr <Service IPv4 range>
1
2
3
4
5
6
7
8
9
10
11
12
13
14
15
16
17
18
19
20
21
22
23
24
25
26
27
28
29
30
31
32
33
34
35
MIME-Version: 1.0
Content-Type: multipart/mixed; boundary="BOUNDARY"

--BOUNDARY
Content-Type: application/node.eks.aws

---
apiVersion: node.eks.aws/v1alpha1
kind: NodeConfig
spec:
  cluster:
    name: <cluster name>
    apiServerEndpoint: <API server endpoint>
    certificateAuthority: <Certificate authority>
    cidr: <Service IPv4 range , get this from the networking tab in the eks console>
  kubelet:
    maxPods: 100
    containerRuntime: containerd
    config:
      kind: KubeletConfiguration
      apiVersion: kubelet.config.k8s.io/v1beta1
      registerWithTaints:
        - key: special-nodegroup
          value: <group name>
          effect: NoSchedule
    flags:
      - --node-labels=group=<group name>,alpha.eksctl.io/nodegroup-name=<group name>
  networking:
    ipFamily: ipv4
  containerd:
    configPatches:
      - |-
        [plugins."io.containerd.grpc.v1.cri".containerd]
          default_runtime_name = "runc"
--BOUNDARY--
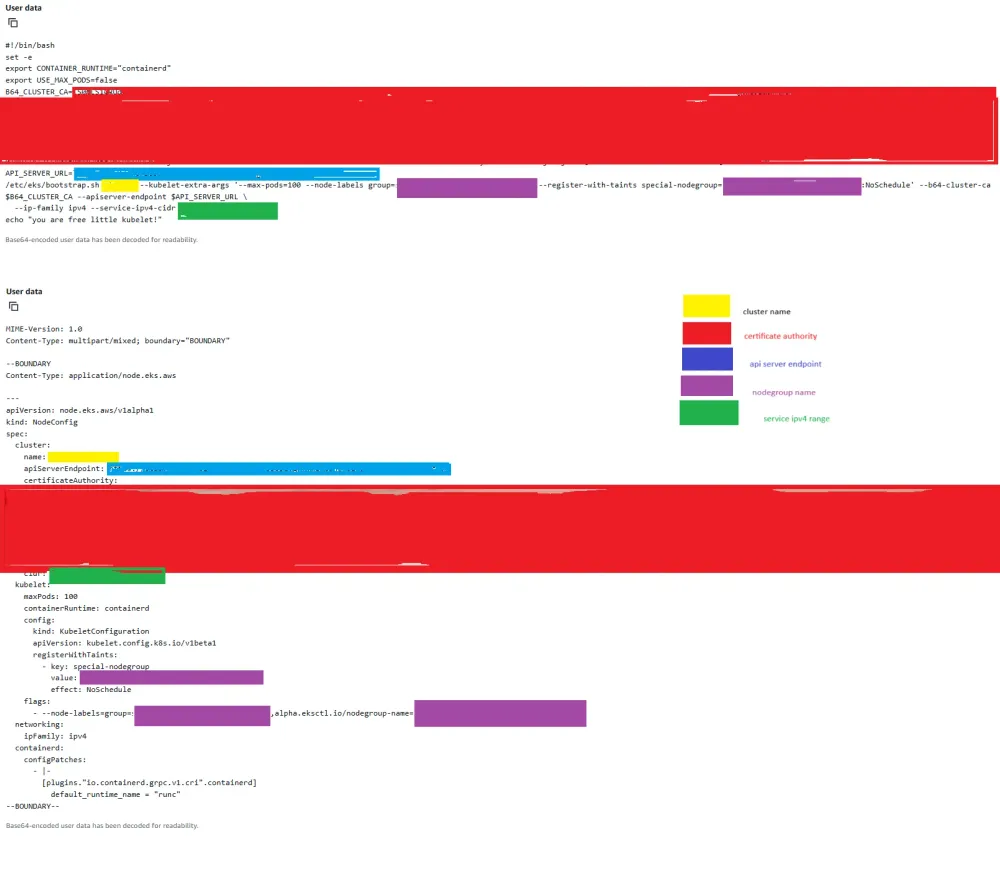
as you can see , the new MIME type file is more readable and allows for more customizations , now let's visually convert the old script to the new one
don't forget to update your cluster add-ons and to do an instance refresh to get nodes with the latest launch template .
read the article i wrote about using the lambda web adapter here and follow me on LinkedIn . thanks for reading .
Enjoyed reading this content? Let the author know!
Your likes, comments, shares, and saves help creators reach more builders.

Loading recommendations
Loading article