

Using Terraform to create AWS IoT Things
In this post users will learn to use Terraform to create AWS IoT Certificates and a Policy attached to the Certificates and create AWS IoT Things created with these Certificates attached.


Terraform is a widely using Infrastructure as Code tool to manage Cloud infrastructure. This post will introduce you to use Terraform as Infrastructure-as-Code (IaC) tool to create 1/ IoT Policy, 2/ a new Certificate with the IoT policy attached to this Certificate, and 3/ create an IoT Thing with the Certificate attached.
Terraform code shared in this github repository will help you create unique Certificates for each IoT Thing defined in the configuration file. A template of IoT policy created is shown in the code block. It enforces to publish & subscribe to a topic defined in the code as shown in the code block, and connect with thing name used while creating IoT Thing.
{ "Statement": [ { "Action": "iot:Connect", "Effect": "Allow", "Resource": "arn:aws:iot:REGION:ACCOUNT_NUMBER:client/${iot:Connection.Thing.ThingName}", "Sid": "ClientConnectRestrictred" }, { "Action": [ "iot:Receive", "iot:Publish" ], "Effect": "Allow", "Resource": "arn:aws:iot:REGION:ACCOUNT_NUMBER:topic/TOPIC_NAME/${iot:Connection.Thing.ThingName}", "Sid": "PublishReceivePermissions" }, { "Action": "iot:Subscribe", "Effect": "Allow", "Resource": "arn:aws:iot:REGION:ACCOUNT_NUMBER:topicfilter/TOPIC_NAME/${iot:Connection.Thing.ThingName}", "Sid": "SubscribePermissions" } ], "Version": "2012-10-17"}IoT devices connect to AWS IoT Core using these certificates, hence we create a unique certificate for each device. Policy defined in the code improves security. This policy will allow IoT devices connect to AWS IoT core using MQTT ClientID with the thing name defined. This policy also enforces Publish and Subscribe to a topic as defined in the Resource section of the Statement in the code block.
Note: Certificates are stored as sensitive data in Terraform state file and Terraform output command can be used to retrieve these Certificates.
Prerequisites:
- An active AWS account.
- AWS Command Line Interface (AWS CLI) configured.
- Set the AWS environment variables ‘AWS_ACCESS_KEY_ID‘, ‘AWS_SECRET_ACCESS_KEY‘, ‘AWS_SESSION_TOKEN‘ and ‘AWS_DEFAULT_REGION‘.
- Use this link to learn more about setting Environment variables.
- git and Terraform installed.
To use this code in production environment all the Terraform state files should be stored in Amazon Simple Storage Service (Amazon S3) buckets, a Git repo or other secure storage. Enable versioning when using S3 buckets.
Steps to create IoT things using this repo
- Verify AWS Environment variables are set and check the role assumed.
bash-5.2$ aws sts get-caller-identity{ "UserId": "ARORABOBATEAMANGO2NP:atulchaudhari", "Account": "202406231234", "Arn": "arn:aws:sts::202406231234:assumed-role/IoTAdmin/atulchaudhari"}- Create a tfvars file as shown below with AWS Account number and AWS region where the AWS IoT things and certificates need to be created. Set the name of the AWS IoT Policy that should be created and attached to the AWS IoT X.509 certificates that will be created. Set the AWS IoT MQTT Topic to which the IoT Things can publish and subscribe using the Certificate and the Policy.
region = "us-west-2"account = "202406231234"thing_policy = "demoterraformpolicy"topic = "demoterraformtopic"thing = ["thing01", "thing02", "thing03"]In this example.tfvars file 3 IoT things are requested to be created with Policy name "demoterraformpolicy" and MQTT topic "demoterraformtopic"
- Next run
ls -lhto confirm the terraform files and the tfvars file are in the current working directory.
bash-5.2$ ls -lhtotal 96-rw-r--r-- 1 atulac staff 1.0K Jun 23 22:34 LICENSE-rw-r--r-- 1 atulac staff 21K Jun 23 22:40 README.md-rw-r--r-- 1 atulac staff 1.1K Jun 23 22:24 data.tf-rw-r--r-- 1 atulac staff 193B Jun 23 23:35 example.tfvarsdrwxr-xr-x 7 atulac staff 224B Jun 23 22:24 images-rw-r--r-- 1 atulac staff 854B Jun 23 22:24 main.tf-rw-r--r-- 1 atulac staff 662B Jun 23 22:24 output.tf-rw-r--r-- 1 atulac staff 400B Jun 23 22:24 variables.tf- Run
terraform initto initialize the download required provider packages. Your terminal output should look as shown below:
Initializing the backend...
Initializing provider plugins...- Finding latest version of hashicorp/aws...- Finding latest version of hashicorp/http...- Installing hashicorp/aws v5.55.0...- Installed hashicorp/aws v5.55.0 (signed by HashiCorp)- Installing hashicorp/http v3.4.3...- Installed hashicorp/http v3.4.3 (signed by HashiCorp)
Terraform has created a lock file .terraform.lock.hcl to record the providerselections it made above. Include this file in your version control repositoryso that Terraform can guarantee to make the same selections by default whenyou run "terraform init" in the future.
Terraform has been successfully initialized!
You may now begin working with Terraform. Try running "terraform plan" to seeany changes that are required for your infrastructure. All Terraform commandsshould now work.
If you ever set or change modules or backend configuration for Terraform,rerun this command to reinitialize your working directory. If you forget, othercommands will detect it and remind you to do so if necessary.- You can run
terraform plan -var-file=example.tfvarsto review the resources that will be created before creating these resources.
bash-5.2$ terraform plan -var-file=example.tfvars data.http.AmazonRootCA1: Reading...data.http.AmazonRootCA1: Read complete after 0s [id=https://www.amazontrust.com/repository/AmazonRootCA1.pem]data.aws_iam_policy_document.aws_iot_thing_policy: Reading...data.aws_iot_endpoint.thing_ats_mqtt: Reading...data.aws_iam_policy_document.aws_iot_thing_policy: Read complete after 0s [id=4035393401]data.aws_iot_endpoint.thing_ats_mqtt: Read complete after 1s [id=atulcommblog-ats.iot.us-west-2.amazonaws.com]
Terraform used the selected providers to generate the following execution plan. Resource actions are indicated with the following symbols:  + create
Terraform will perform the following actions:
  # aws_iot_certificate.thing[0] will be created  + resource "aws_iot_certificate" "thing" {      + active            = true      + arn               = (known after apply)      + ca_certificate_id = (known after apply)      + certificate_pem   = (sensitive value)      + id                = (known after apply)      + private_key       = (sensitive value)      + public_key        = (sensitive value)    }
  # aws_iot_certificate.thing[1] will be created  + resource "aws_iot_certificate" "thing" {      + active            = true      + arn               = (known after apply)      + ca_certificate_id = (known after apply)      + certificate_pem   = (sensitive value)      + id                = (known after apply)      + private_key       = (sensitive value)      + public_key        = (sensitive value)    }
  # aws_iot_certificate.thing[2] will be created
  ...  ...
    # aws_iot_policy.thing will be created  + resource "aws_iot_policy" "thing" {      + arn                = (known after apply)      + default_version_id = (known after apply)      + id                 = (known after apply)      + name               = "demoterraformpolicy"      + policy             = jsonencode(            {              + Statement = [                  + {                      + Action   = "iot:Connect"                      + Effect   = "Allow"                      + Resource = "arn:aws:iot:us-west-2:202406231234:client/${iot:Connection.Thing.ThingName}"                      + Sid      = "ClientConnectRestrictred"                    },                  + {                      + Action   = [                          + "iot:Receive",                          + "iot:Publish",                        ]                      + Effect   = "Allow"                      + Resource = "arn:aws:iot:us-west-2:202406231234:topic/demoterraformtopic/${iot:Connection.Thing.ThingName}"                      + Sid      = "PublishReceivePermissions"                    },                  + {                      + Action   = "iot:Subscribe"                      + Effect   = "Allow"                      + Resource = "arn:aws:iot:us-west-2:202406231234:topicfilter/demoterraformtopic/${iot:Connection.Thing.ThingName}"                      + Sid      = "SubscribePermissions"                    },                ]              + Version   = "2012-10-17"            }        )      + tags_all           = (known after apply)    }...... Plan: 13 to add, 0 to change, 0 to destroy.
Changes to Outputs: + AmazonRootCA1_response = <<-EOT -----BEGIN CERTIFICATE----- MIIDQTCCAimgAwIBAgITBmyfz5m/jAo54vB4ikPmljZbyjANBgkqhkiG9w0BAQsF ADA5MQswCQYDVQQGEwJVUzEPMA0GA1UEChMGQW1hem9uMRkwFwYDVQQDExBBbWF6 b24gUm9vdCBDQSAxMB4XDTE1MDUyNjAwMDAwMFoXDTM4MDExNzAwMDAwMFowOTEL ... ... 5MsI+yMRQ+hDKXJioaldXgjUkK642M4UwtBV8ob2xJNDd2ZhwLnoQdeXeGADbkpy rqXRfboQnoZsG4q5WTP468SQvvG5 -----END CERTIFICATE----- EOT + iot_endpoint = "atulcommblog-ats.iot.us-west-2.amazonaws.com" + iot_topic = "demoterraformtopic" + thing_arn = [ + (known after apply), + (known after apply), + (known after apply), ] + thing_cert = (sensitive value) + thing_cert_pubkey = (sensitive value) + thing_name = [ + "thing01", + "thing02", + "thing03", ] + thing_pvtkey = (sensitive value)- Finally create the AWS IoT Things using Terraform with
terraform apply -var-file=example.tfvars -auto-approve
bash-5.2$ terraform apply -var-file=example.tfvars -auto-approvedata.http.AmazonRootCA1: Reading...data.http.AmazonRootCA1: Read complete after 0s [id=https://www.amazontrust.com/repository/AmazonRootCA1.pem]data.aws_iam_policy_document.aws_iot_thing_policy: Reading...data.aws_iot_endpoint.thing_ats_mqtt: Reading...data.aws_iam_policy_document.aws_iot_thing_policy: Read complete after 0s [id=1649382831]data.aws_iot_endpoint.thing_ats_mqtt: Read complete after 0s .........
Apply complete! Resources: 13 added, 0 changed, 0 destroyed.
Outputs:
AmazonRootCA1_response = <<EOT-----BEGIN CERTIFICATE-----MIIDQTCCAimgAwIBAgITBmyfz5m/jAo54vB4ikPmljZbyjANBgkqhkiG9w0BAQsFADA5MQswCQYDVQQGEwJVUzEPMA0GA1UEChMGQW1hem9uMRkwFwYDVQQDExBBbWF6b24gUm9vdCBDQSAxMB4XDTE1MDUyNjAwMDAwMFoXDTM4MDExNzAwMDAwMFowOTELMAkGA1UEBhMCVVMxDzANBgNVBAoTBkFtYXpvbjEZMBcGA1UEAxMQQW1hem9uIFJvb3QgQ0EgMTCCASIwDQYJKoZIhvcNAQEBBQADggEPADCCAQoCggEBALJ4gHHKeNXjca9HgFB0fW7Y14h29Jlo91ghYPl0hAEvrAIthtOgQ3pOsqTQNroBvo3bSMgHFzZM9O6II8c+6zf1tRn4SWiw3te5djgdYZ6k/oI2peVKVuRF4fn9tBb6dNqcmzU5L/qwIFAGbHrQgLKm+a/sRxmPUDgH3KKHOVj4utWp+UhnMJbulHheb4mjUcAwhmahRWa6VOujw5H5SNz/0egwLX0tdHA114gk957EWW67c4cX8jJGKLhD+rcdqsq08p8kDi1L93FcXmn/6pUCyziKrlA4b9v7LWIbxcceVOF34GfID5yHI9Y/QCB/IIDEgEw+OyQmjgSubJrIqg0CAwEAAaNCMEAwDwYDVR0TAQH/BAUwAwEB/zAOBgNVHQ8BAf8EBAMCAYYwHQYDVR0OBBYEFIQYzIU07LwMlJQuCFmcx7IQTgoIMA0GCSqGSIb3DQEBCwUAA4IBAQCY8jdaQZChGsV2USggNiMOruYou6r4lK5IpDB/G/wkjUu0yKGX9rbxenDIU5PMCCjjmCXPI6T53iHTfIUJrU6adTrCC2qJeHZERxhlbI1Bjjt/msv0tadQ1wUsN+gDS63pYaACbvXy8MWy7Vu33PqUXHeeE6V/Uq2V8viTO96LXFvKWlJbYK8U90vvo/ufQJVtMVT8QtPHRh8jrdkPSHCa2XV4cdFyQzR1bldZwgJcJmApzyMZFo6IQ6XU5MsI+yMRQ+hDKXJioaldXgjUkK642M4UwtBV8ob2xJNDd2ZhwLnoQdeXeGADbkpyrqXRfboQnoZsG4q5WTP468SQvvG5-----END CERTIFICATE-----
EOTiot_endpoint = "atulcommblog-ats.iot.us-west-2.amazonaws.com"iot_topic = "demoterraformtopic"thing_arn = [ "arn:aws:iot:us-west-2:202406231234:thing/thing01", "arn:aws:iot:us-west-2:202406231234:thing/thing02", "arn:aws:iot:us-west-2:202406231234:thing/thing03",]thing_cert = <sensitive>thing_cert_pubkey = <sensitive>thing_name = [ "thing01", "thing02", "thing03",]thing_pvtkey = <sensitive>- Let's verify them in AWS Console by Login to AWS Console and search for AWS IoT core in search and set the region to US-WEST-2. Expand All devices menu in the left sidebar and click on Things. You should see the newly created Things as listed in the example.tfvars file.
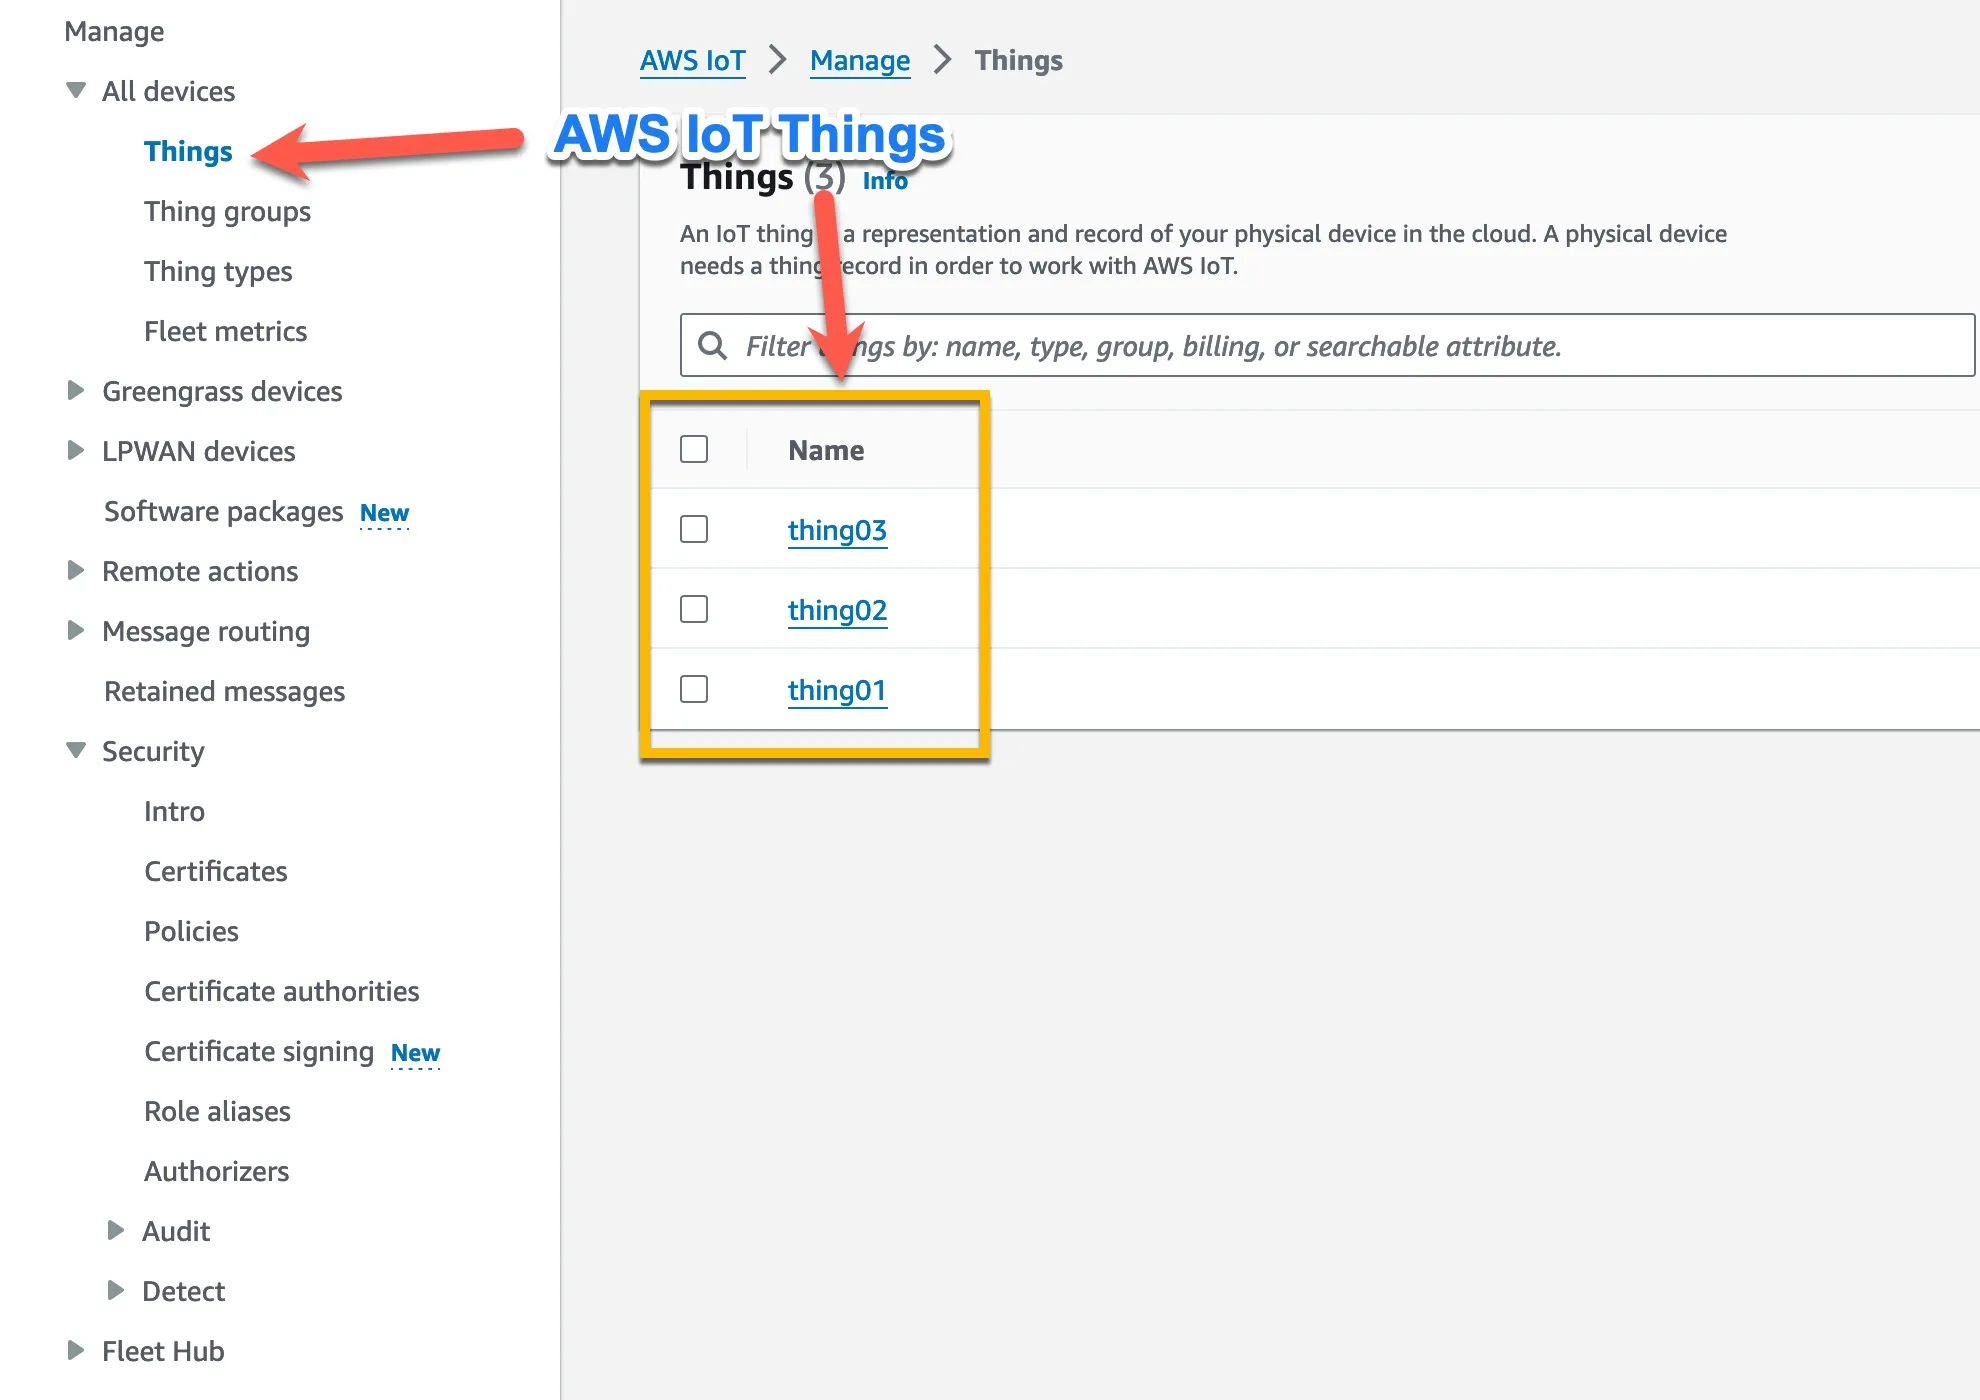
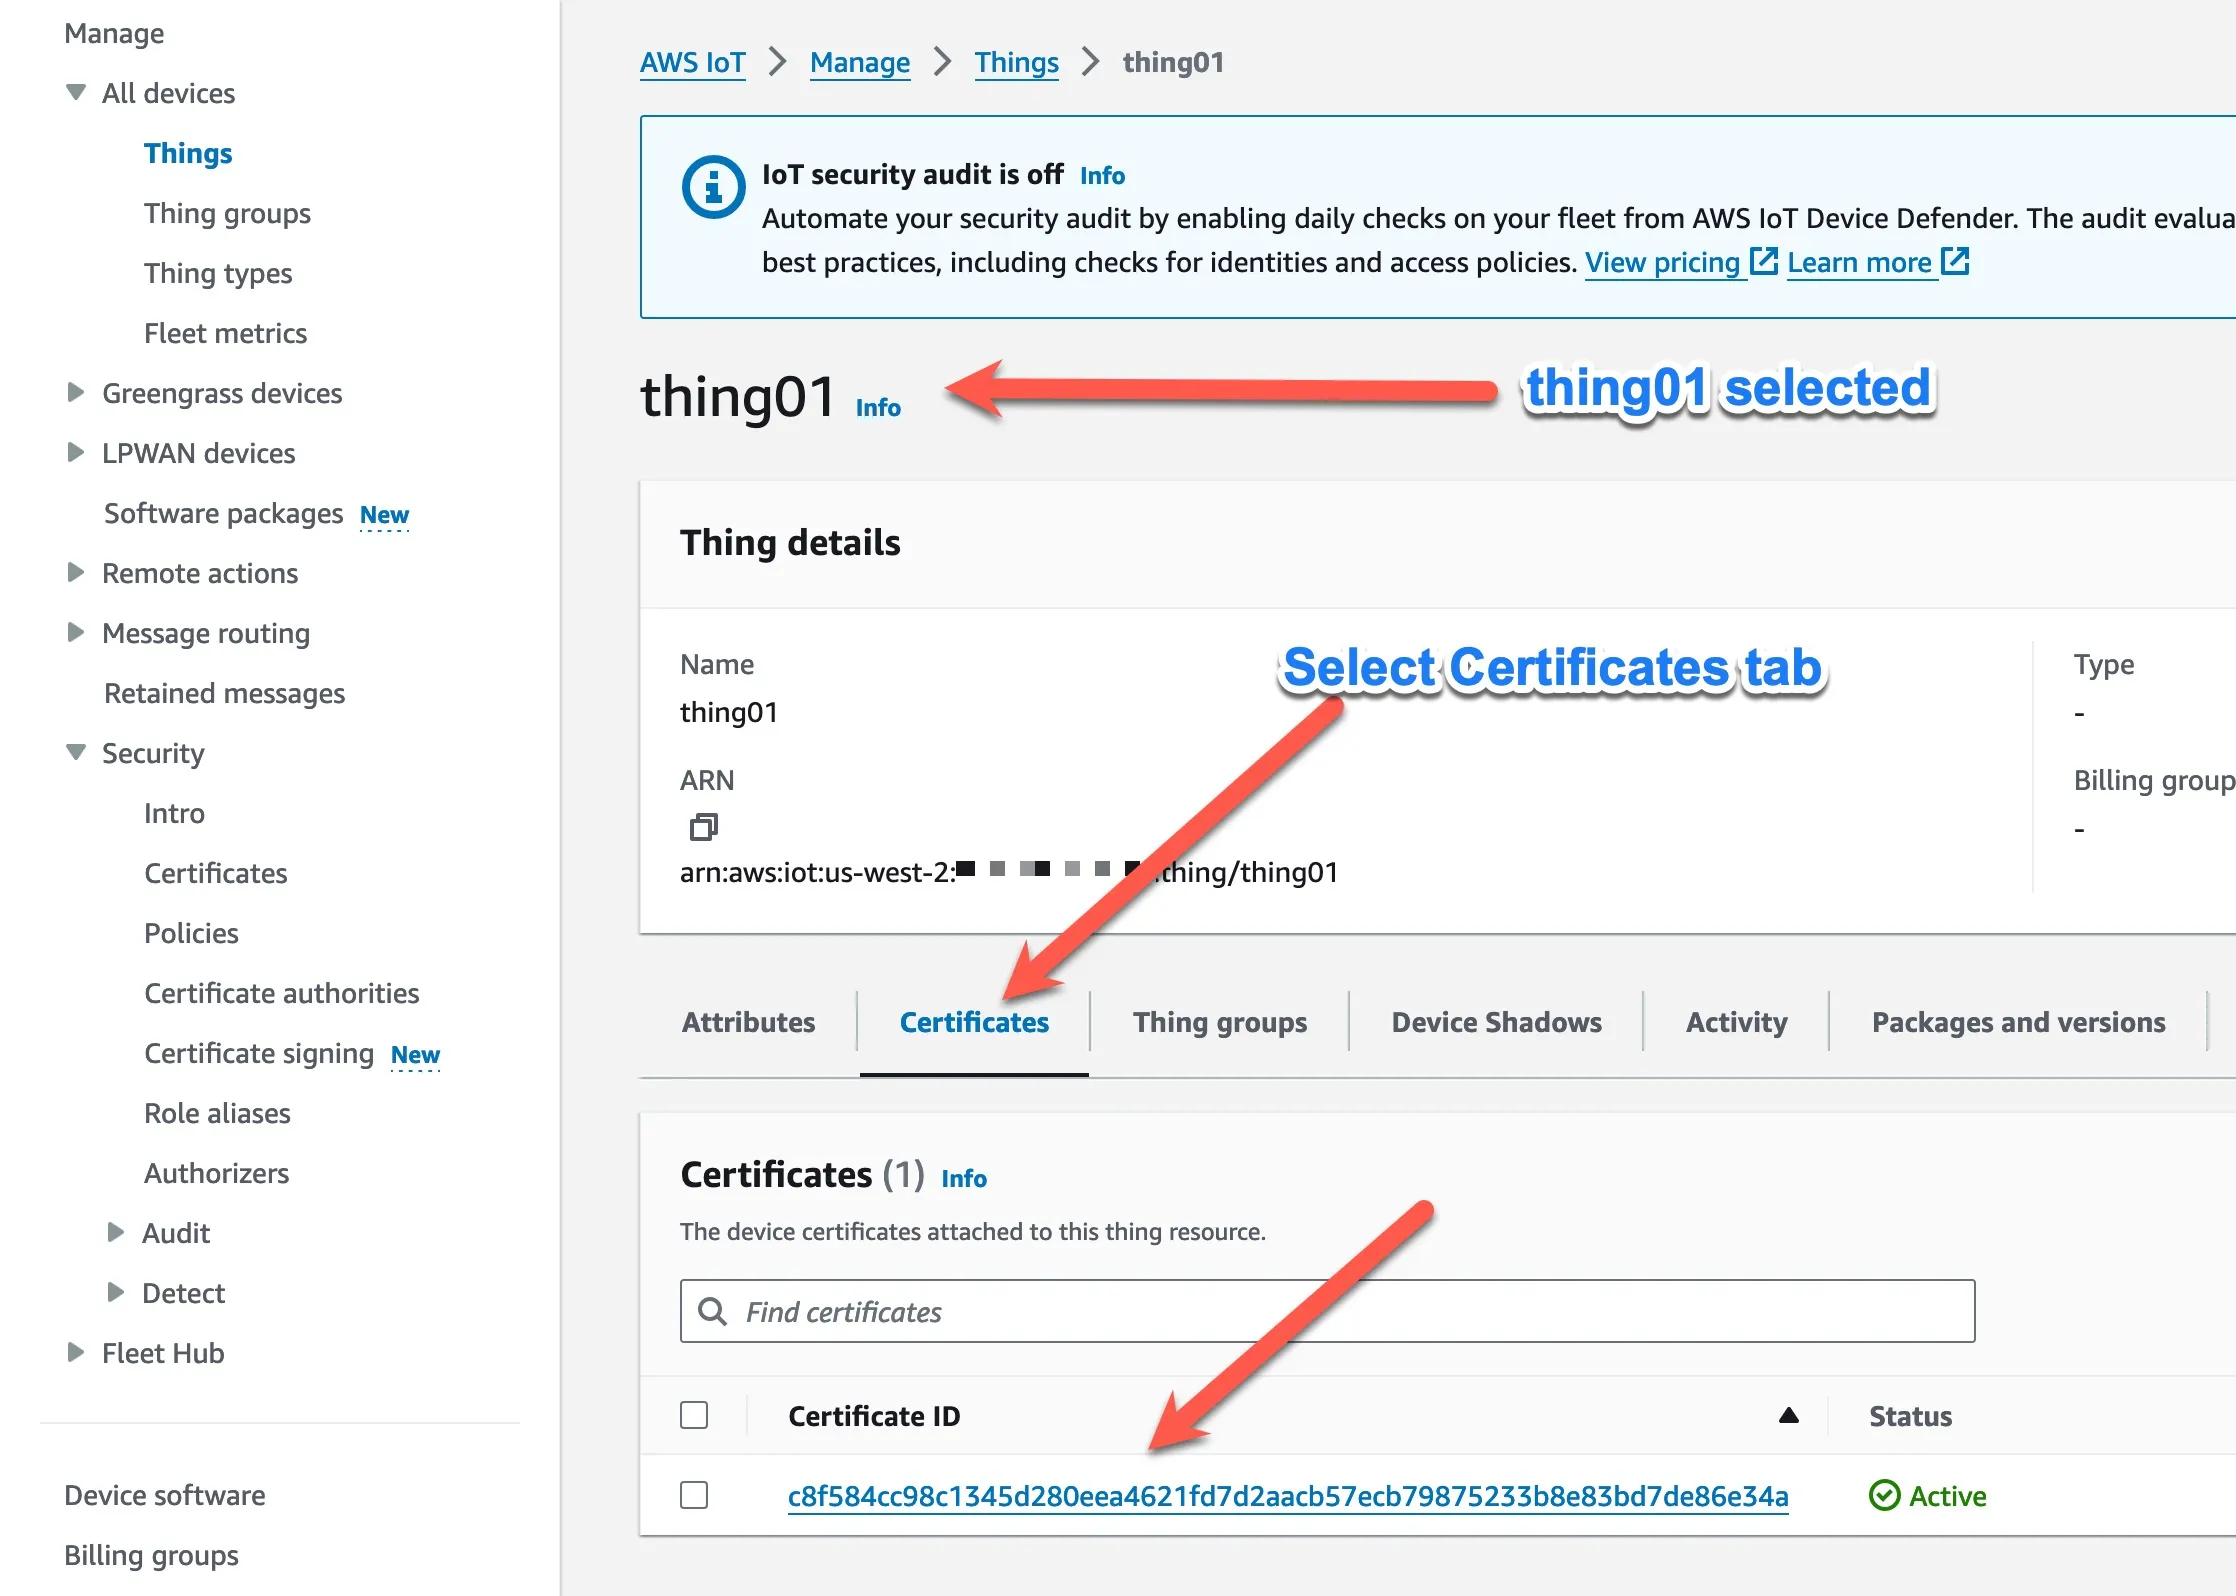
- Click on thing01 to review the Thing created and the Certificate attached. Next click on the certificate id as shown in the screenshot below:
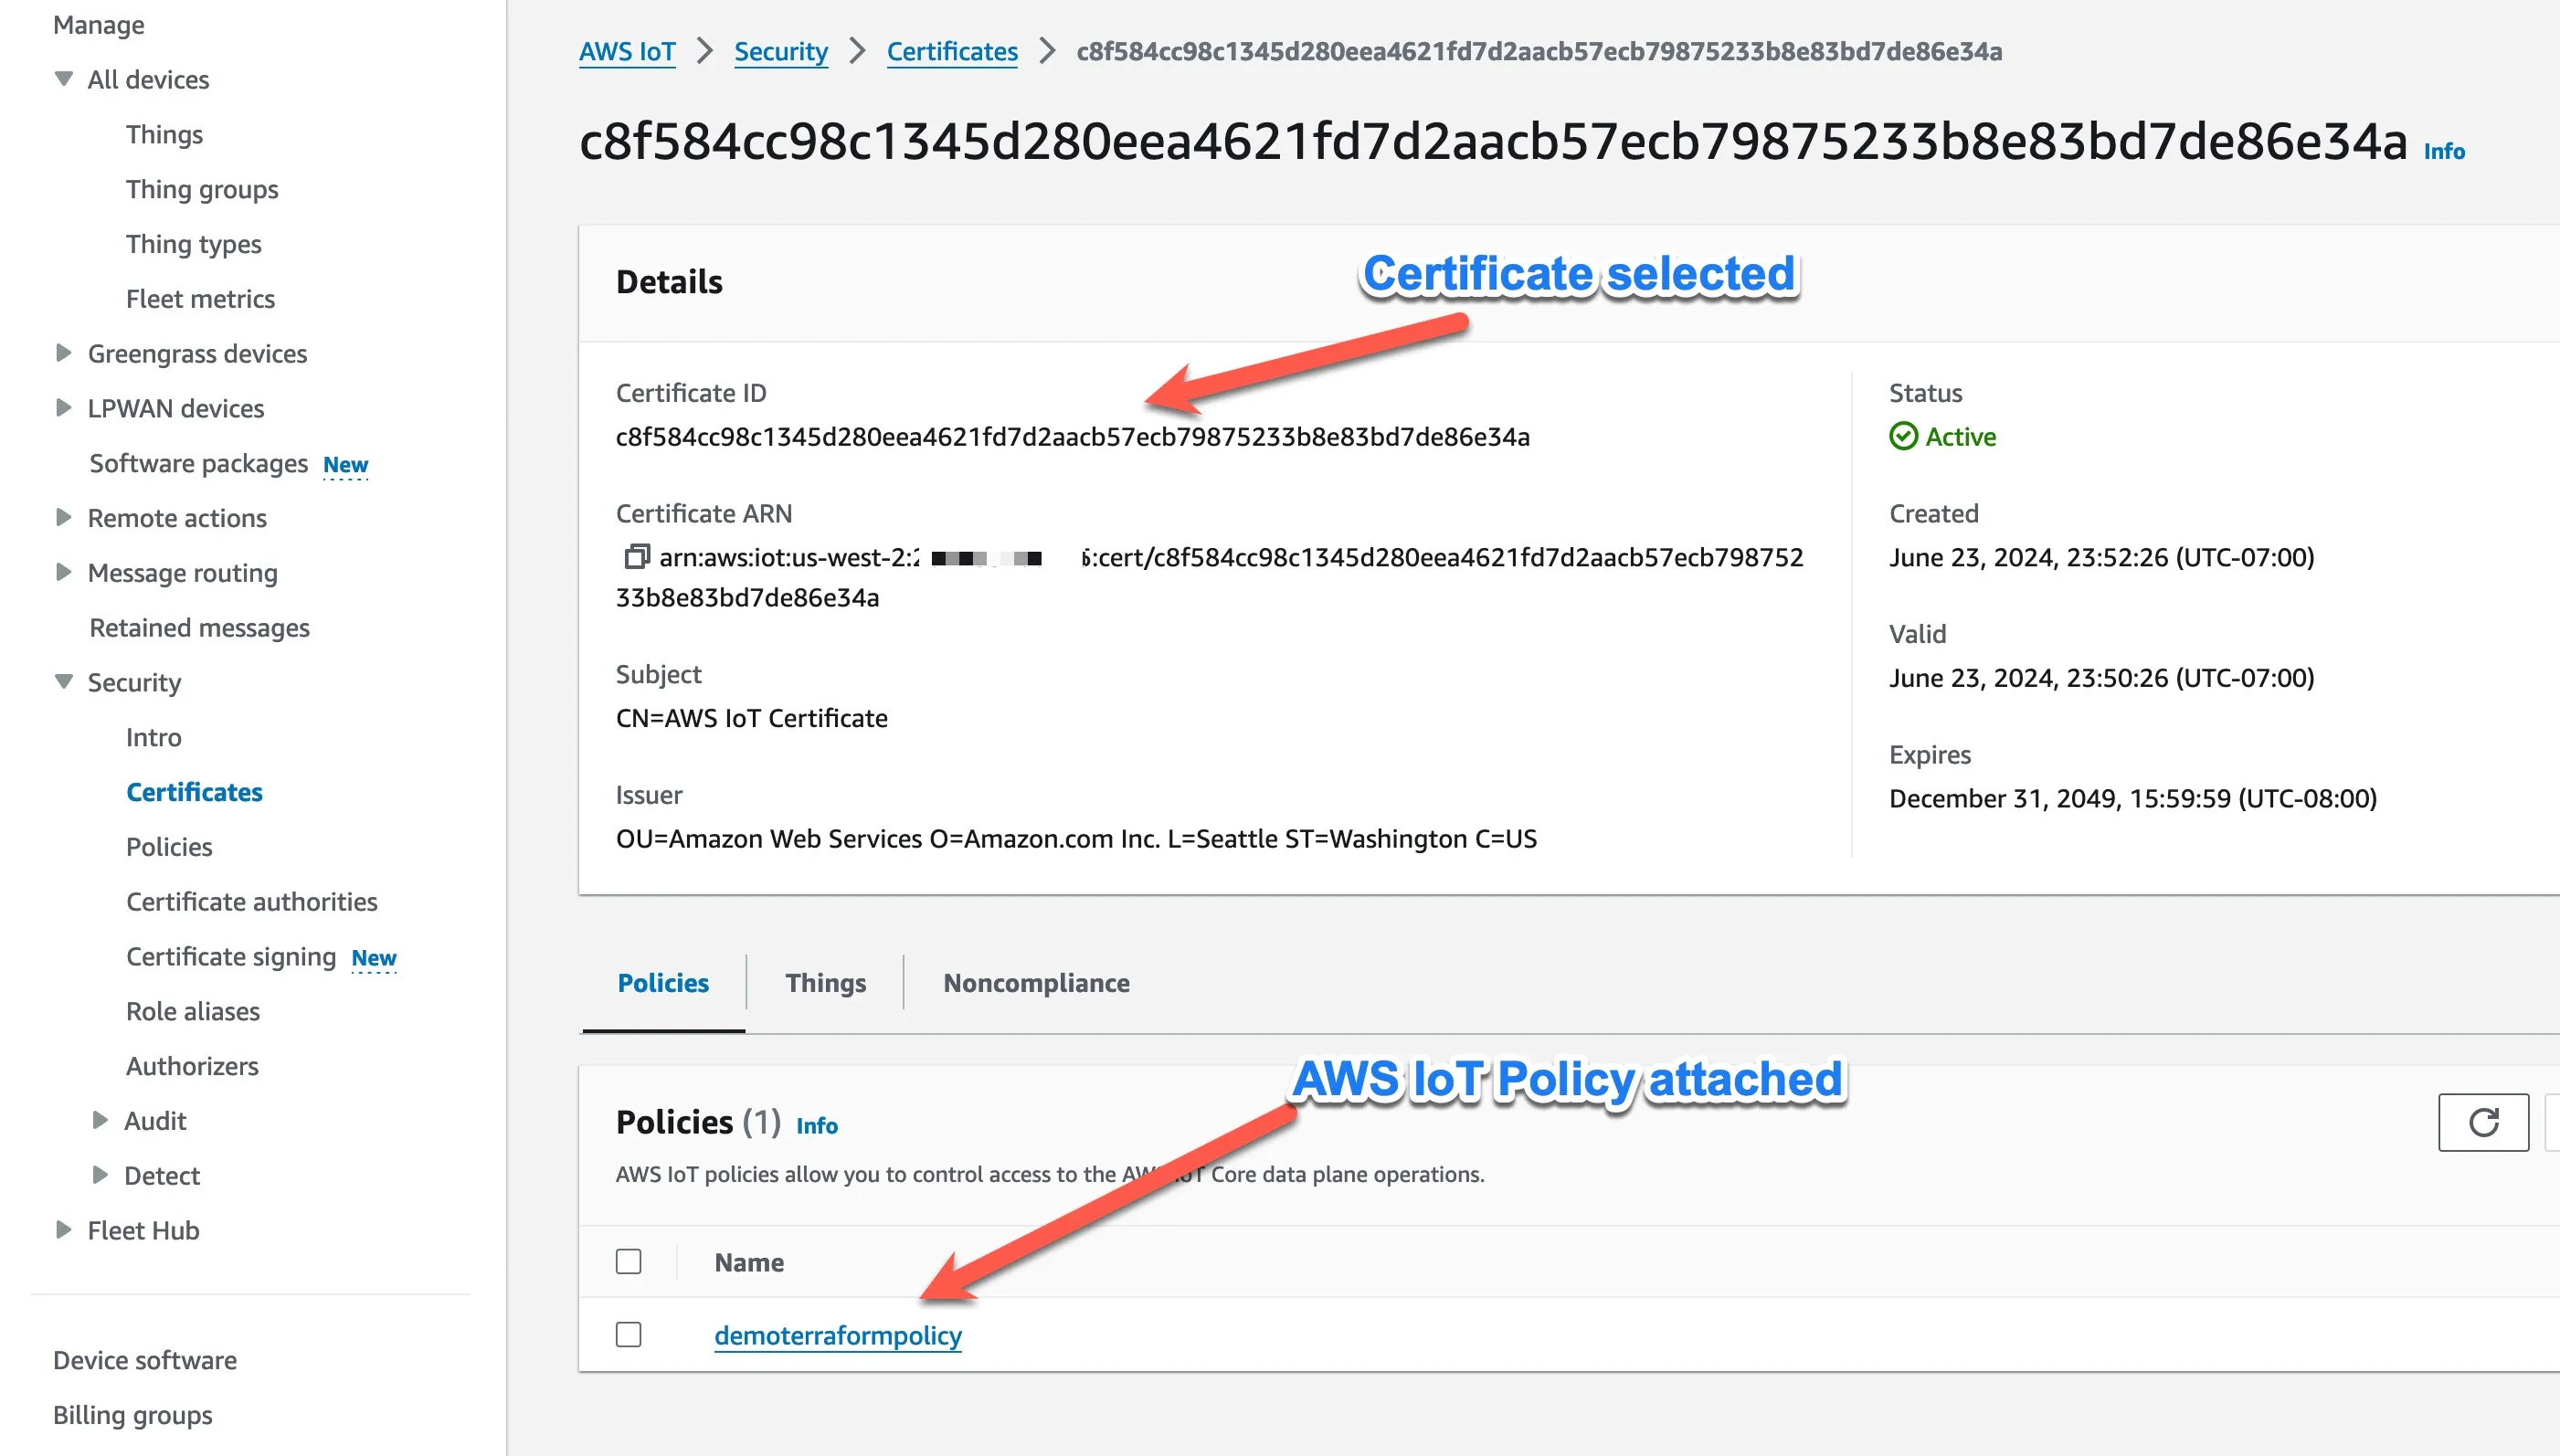
- Certificate shows the AWS IoT policy created as defined in the terraform scripts and attached to AWS IoT Thing thing01.
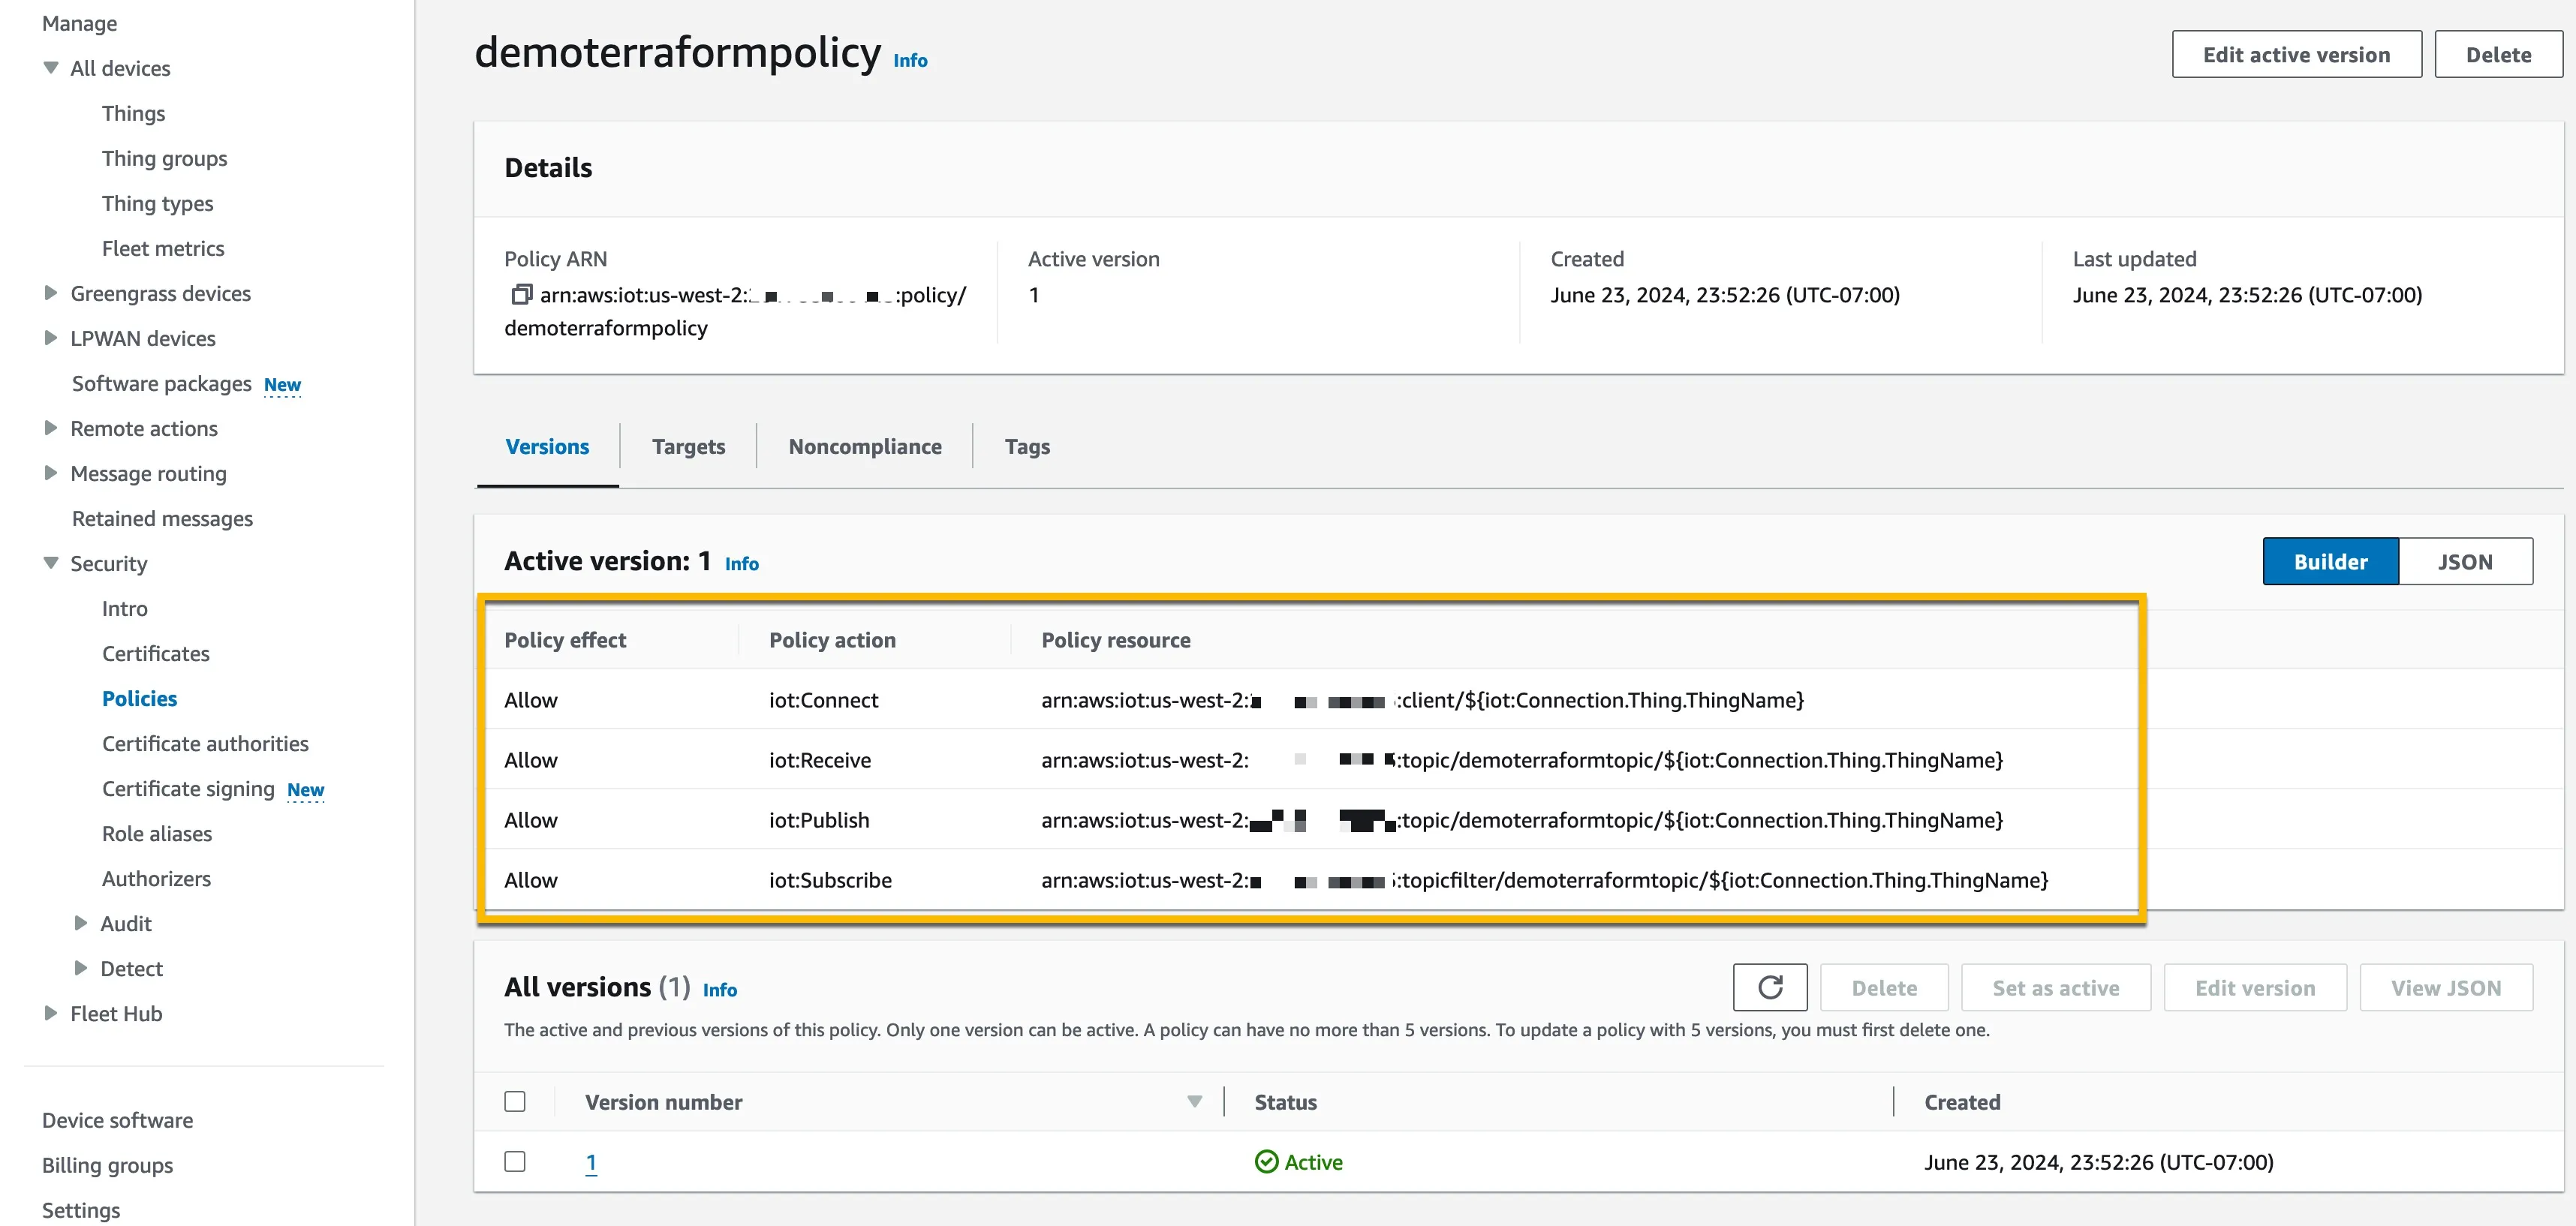
- The new Policy created shows the permissions as defined in the data.tf terraform file with permissions to allow Connect, Receive, Publish and Subscribe.
- Next the Root CA1 and the AWS IoT Things certificates can be extracted from the output file using these commands
-
terraform output -json | jq -r '.AmazonRootCA1_response.value'to show the Amazon Root CA1.
-
terraform output -json | jq -r '.thing_cert.value[]'to show the list of X.509 certificates.
-
terraform output -json | jq -r '.thing_pvtkey.value[]'to show the list of private certificates.
bash-5.2$ terraform output -json | jq -r '.AmazonRootCA1_response.value'-----BEGIN CERTIFICATE-----MIIDQTCCAimgAwIBAgITBmyfz5m/jAo54vB4ikPmljZbyjANBgkqhkiG9w0BAQsFADA5MQswCQYDVQQGEwJVUzEPMA0GA1UEChMGQW1hem9uMRkwFwYDVQQDExBBbWF6b24gUm9vdCBDQSAxMB4XDTE1MDUyNjAwMDAwMFoXDTM4MDExNzAwMDAwMFowOTELMAkGA1UEBhMCVVMxDzANBgNVBAoTBkFtYXpvbjEZMBcGA1UEAxMQQW1hem9uIFJvb3QgQ0EgMTCCASIwDQYJKoZIhvcNAQEBBQADggEPADCCAQoCggEBALJ4gHHKeNXjca9HgFB0fW7Y14h29Jlo91ghYPl0hAEvrAIthtOgQ3pOsqTQNroBvo3bSMgHFzZM9O6II8c+6zf1tRn4SWiw3te5djgdYZ6k/oI2peVKVuRF4fn9tBb6dNqcmzU5L/qwIFAGbHrQgLKm+a/sRxmPUDgH3KKHOVj4utWp+UhnMJbulHheb4mjUcAwhmahRWa6VOujw5H5SNz/0egwLX0tdHA114gk957EWW67c4cX8jJGKLhD+rcdqsq08p8kDi1L93FcXmn/6pUCyziKrlA4b9v7LWIbxcceVOF34GfID5yHI9Y/QCB/IIDEgEw+OyQmjgSubJrIqg0CAwEAAaNCMEAwDwYDVR0TAQH/BAUwAwEB/zAOBgNVHQ8BAf8EBAMCAYYwHQYDVR0OBBYEFIQYzIU07LwMlJQuCFmcx7IQTgoIMA0GCSqGSIb3DQEBCwUAA4IBAQCY8jdaQZChGsV2USggNiMOruYou6r4lK5IpDB/G/wkjUu0yKGX9rbxenDIU5PMCCjjmCXPI6T53iHTfIUJrU6adTrCC2qJeHZERxhlbI1Bjjt/msv0tadQ1wUsN+gDS63pYaACbvXy8MWy7Vu33PqUXHeeE6V/Uq2V8viTO96LXFvKWlJbYK8U90vvo/ufQJVtMVT8QtPHRh8jrdkPSHCa2XV4cdFyQzR1bldZwgJcJmApzyMZFo6IQ6XU5MsI+yMRQ+hDKXJioaldXgjUkK642M4UwtBV8ob2xJNDd2ZhwLnoQdeXeGADbkpyrqXRfboQnoZsG4q5WTP468SQvvG5-----END CERTIFICATE-----
bash-5.2$ terraform output -json | jq -r '.thing_cert.value[]'-----BEGIN CERTIFICATE-----MIIDWTCCAkGgAwIBAgIUdjxXCi5OG6z9MTcsRL6dzSQ9YBgwDQYJKoZIhvcNAQELBQAwTTFLMEkGA1UECwxCQW1hem9uIFdlYiBTZXJ2aWNlcyBPPUFtYXpvbi5jb20gSW5jLiBMPVNlYXR0bGUgU1Q9V2FzaGluZ3RvbiBDPVVTMB4XDTI0MDYyNDA2NTAyNloXDTQ5MTIzMTIzNTk1OVowHjEcMBoGA1UEAwwTQVdTIElvVCBDZXJ0aWZpY2F0ZTCCASIwDQYJKoZIhvcNAQEBBQADggEPADCCAQoCggEBANI2GUMZ4k4yIWHvuDq4Ir0HpwMUynm2RJ+/Je6GQsnyuSZUepW0aTdBtxxXUHFgO56K1qtgx3atcMsR++w8KywGq4FHCarCHvDB2TwZJSJecUUdWU8lMtU3xWKMSsC92hYAVpPteQ2+dHhMXKcE0+z5wBLEutUf9ywHNkDWHSXQNci8UxrxUbIssoqO/fOSNjkBiSdzBJn1pZFREU/dVs1UEcSlMYKBGVi3MdK+zK9yuHhRvIO7nnGCJPExFzXVw8C6/Ih771c51tKjJS6IJq8isUZBTjyrIupLYWl98e8Yd/KTmtY+T761y8/vNUUjUURIvbRZwTos6q5hTMjurucCAwEAAaNgMF4wHwYDVR0jBBgwFoAUs7mTJXwvDm5aP3rISipxGvSorfAwHQYDVR0OBBYEFFkh9RMtRx2dA6KJ2PyNbQzbaFM7MAwGA1UdEwEB/wQCMAAwDgYDVR0PAQH/BAQDAgeAMA0GCSqGSIb3DQEBCwUAA4IBAQCLu9/YhsJQ0PuEsj4cHFZfmNOl2jXVZOB9XBFDXwuvEE/1amnPpMghLY2BC3Tny0IgquAVC5xh49t2xr01YFi2mBbbu+PXC5hQuGgfyx1OSIGlDXXY3UPogPsSa9NfiFtbQc5L/k7AJCUJ43hPYKOCIGL/ZPomUnqm6QHo8JhVd67YMWIV3J6H+pAJZSOsPVTnyLhWaH4+X12qQE8458+q26k2FcDd87sqt0W1gZguOG+ScPW+XdeWp9DlvGj7JNhTcqKiKF0XgTvjyzHWd7Gg8LoDdx+qyc84TBZWRO9DAARHw78ns/RYoEjXiGOHEkf4easYuxkfnzwJ5yZvytry-----END CERTIFICATE-----
-----BEGIN CERTIFICATE-----MIIDWTCCAkGgAwIBAgIUauXHFfFxGsRCEJcdwJ28BGOhxm4wDQYJKoZIhvcNAQELBQAwTTFLMEkGA1UECwxCQW1hem9uIFdlYiBTZXJ2aWNlcyBPPUFtYXpvbi5jb20gSW5jLiBMPVNlYXR0bGUgU1Q9V2FzaGluZ3RvbiBDPVVTMB4XDTI0MDYyNDA2NTAyNloXDTQ5MTIzMTIzNTk1OVowHjEcMBoGA1UEAwwTQVdTIElvVCBDZXJ0aWZpY2F0ZTCCASIwDQYJKoZIhvcNAQEBBQADggEPADCCAQoCggEBALkMORcfB8AJ/DYbtCGxbz+MPP+/0WdyT/ROaAYPFbfcc9DCACuFmQUjhLWl1COJxwOAlYQXB8mJRSa8PGfxQGaHAzS+aGE7lhVPJ5BMMa7RBgnQLqUdK0TzQpasTcW068QCg77bc3gVq/jnFghUWFnRvReQzWncbC1rDUUME4pBsMOkoJp65JY6OndR+z3Ipb6U7r+nwuj6rZJG2i6s+8Ka/6xMfnLBKzuuZIyW0tpW4o014MU+uSYY7w9Yg64+QK4BwdegqLTVIzfQec6y68/IUSFdMq9JWhFoX7QzwufjqzMWHKpit1EwarcyUDqbKlmShCCWgoQtmPaS7KGf7AcCAwEAAaNgMF4wHwYDVR0jBBgwFoAUae1G19MNHrApsK8MpL3k9pDTGuUwHQYDVR0OBBYEFGcvDMkZ63WFgT+HO4nwD0E8WoPSMAwGA1UdEwEB/wQCMAAwDgYDVR0PAQH/BAQDAgeAMA0GCSqGSIb3DQEBCwUAA4IBAQAoxqYqtSlBwqpYJG8MgADsOCYB9mbY3CdgP2uxNcYRYRbWAJVx5y+PG9j/3rPqB20u9A4Na1LcXOflNtKiQbQ0Hqc6texkM+ffh3jBlbANHt13H1g2SKq2Q+YFfCH+e4BvJ2UEnK3RXV/uiPLQwmvY4bGS+Is9syWcZ0GJhLCC+SqE0n5YXfpFufSSAmfxz/p5BPpy6DZuosnZVl5JB1Q7m9Dj6ja5D6bI4PM0uxMbozO6CU27lvWNfsGE4IHFTqYY1Y7TCGgGupUcsO5DZLz3l21k7Dl/iZxvsK7NSoJWNwn1zwCP8eH9WoK6oLOGNQU/RGJ0dWZOigb9LWrW7cCS-----END CERTIFICATE-----
-----BEGIN CERTIFICATE-----MIIDWjCCAkKgAwIBAgIVAMBxU8Q9LoXmfNp3enHvqNFRAPBEMA0GCSqGSIb3DQEBCwUAME0xSzBJBgNVBAsMQkFtYXpvbiBXZWIgU2VydmljZXMgTz1BbWF6b24uY29tIEluYy4gTD1TZWF0dGxlIFNUPVdhc2hpbmd0b24gQz1VUzAeFw0yNDA2MjQwNjUwMjZaFw00OTEyMzEyMzU5NTlaMB4xHDAaBgNVBAMME0FXUyBJb1QgQ2VydGlmaWNhdGUwggEiMA0GCSqGSIb3DQEBAQUAA4IBDwAwggEKAoIBAQDYt6aUhppry9tQeAOZ0Rp+Tcf+le0UQ79RO5V0CLWCjWV9+WmFC6N2HUe2qC/9UDSNxmw6muOr3CX6O5jGxQf5EfZy9J/aQgLkxj5fWA2no0KbT5mW9vPhcXuwnK4AflSJGvX5A13yRRte1QeGbLmZG0rMLmOk9dllwIerk1xB+LD5K7IPNoKata6V6isswT1O2TNY+7cLGBW8Q4QThnYSOBNdsno0x7XAZFTWUPV3iAv/kOCW+jI3qZ05JJ5DMo0t1mu/e2DLdICYzqwnCZLU5uR4Li0aySaBjND0y9ldXBFYTzFSvjQXQ8U3Sgi1T9IqvyGNbAcTk9fXRiXQyMiZAgMBAAGjYDBeMB8GA1UdIwQYMBaAFC/MMWIayVPzzSG+H7v/MlbM8L10MB0GA1UdDgQWBBRXoIiqOI7r6ID3mOx4/TY4VJWXkDAMBgNVHRMBAf8EAjAAMA4GA1UdDwEB/wQEAwIHgDANBgkqhkiG9w0BAQsFAAOCAQEAStNr9qEiFv4mpI2M4hLO7ZZ9sZpJi2royxFojqcwRUNpmFM3voXSpVCL12mfFkD3Z8qQFYFOuFf4tx2p1QSPOLKIrpE+RMDl0b7/jue5pU74KD7w9sQApwr+X4PZsdh8dD3AtMFCyxSLMCJWihlcXj9YQG14WJHiVvQY5XM6X9N/5DFTN6CgQ7EJZVYgnf9Ka/gAq0ICKGg0UwfFxR+Ad/RiaSyNXnqRKaUJCDCPKsKYCgUTh/yPUEmhXHMlI6ceBXVNr6WqrohGfmHWC91iQYj3ya6UrB4kjfIUGvnQ9bIj1pE+nHzTnA3jIvQ6gCHBCfJupb6W1yw2nOHxPnEO1g==-----END CERTIFICATE-----
bash-5.2$ terraform output -json | jq -r '.thing_pvtkey.value[]'-----BEGIN RSA PRIVATE KEY-----MIIEpAIBAAKCAQEA0jYZQxniTjIhYe+4OrgivQenAxTKebZEn78l7oZCyfK5JlR6lbRpN0G3HFdQcWA7norWq2DHdq1wyxH77DwrLAargUcJqsIe8MHZPBklIl5xRR1ZTyUy1TfFYoxKwL3aFgBWk+15Db50eExcpwTT7PnAEsS61R/3LAc2QNYdJdA1yLxTGvFRsiyyio7985I2OQGJJ3MEmfWlkVERT91WzVQRxKUxgoEZWLcx0r7Mr3K4eFG8g7uecYIk8TEXNdXDwLr8iHvvVznW0qMlLogmryKxRkFOPKsi6kthaX3x7xh38pOa1j5PvrXLz+81RSNRREi9tFnBOizqrmFMyO6u5wIDAQABAoIBADTFJ+pUYR9ILmErkJANEYtqlF6NpZaQTwHbNmZ+hd20dQ5OPse+Fnusn48ZzDPp+I2ARQuYq/n66EnSJe/T2vKeagd2EdMwEBxYTXRsy4mpM74p8/WOXQhxi7eFiG6COnEzfIh+INl2aj6YzNmQuLLQr4sGn/BIqf//f3sfRQnsmlTpccnpFk1TzfEgmq6IMN+CTM18Hy+oMo4EaJgu607zDYnX/wxHA3tl9XmLc5W+ibkK7vggyEIYhHwf4UeuBBIJQiFNXC04KSUvoBiW3GoOOxq8G3E8v55T63Tp18IJgqiDUEccdkBQzrw+dv7x0bc3c3IWE5+fEbJ262F3ZAECgYEA7NqLtSU3CUlHKdiyJwlXxvs1rznKgzi9PqLQWTDGQDj3MD1xbuaOKZgs38oNqWquY1x1acFjyuEBJz1LARTXo3tTtDrZF+ulKV95Ox2phT2iuDy1cAO/OBbiKB2UnVfhib7wYHEl7wdM4jZrjMbNHz4RGURHC1d7FQjg+640fGcCgYEA4zQ3HEIdngRIAvwzq2vlLDY3NpwLhX28kag/gvU1iEQYt/+9jKQx7cj7ljJBRZt/sCzHuJnjzUunCvNBT5W07wmBm6rR34ikczuh1YXWhgryWt29kLXmXU15YP5mfOzW4XkRkf5SnWPVegvVZLC9Yb9eQMPTohD16AvRI9lEqYECgYEArZfr50M0WDEF4Ey7HdNCK0t46EmB/LT8NskbzRLraqyVtxyBY9fFAAVRdl/frXjMAXUFdRJRcqOAteK9czh0Z5R/H8w1ystiDLW147b0xPwMo92S2VtVreVPsjkj8EI1wkBYa0bil5MRLYbXQqF+O1TBMXSSYWSniB4uzye5vicCgYEAj0B30uhY1i2q3b74MQf5WdPhIhxnI0aw40Gqsb47f2w4DaNAdvF7zYogHoYXI3U0n/bMAjd9Kw6dBslzD2O7zc83mdetNfxoe4NIuWEGbkNupR4UDK6zzXYwppggNHn7zfPQwTUSD8xHaAkYBcFt1ribC8isog2BjkoNFkZCBYECgYBDrnyqelCrKXChqvDXgtoTArHn4j5q85wGHLzvwMHGRoEchJl3rnHGzHiogyNacQIXb4OOa8ytPns8nCz+TIZkgszAObwr8ssAaSHT1mH6aBWRGErbam1TfrxqPulYiA7lgPcqp4RB2UgIdaGJsmPxL8qiJPVqMVaQKr/ZhBtr9Q==-----END RSA PRIVATE KEY-----
-----BEGIN RSA PRIVATE KEY-----MIIEpAIBAAKCAQEAuQw5Fx8HwAn8Nhu0IbFvP4w8/7/RZ3JP9E5oBg8Vt9xz0MIAK4WZBSOEtaXUI4nHA4CVhBcHyYlFJrw8Z/FAZocDNL5oYTuWFU8nkEwxrtEGCdAupR0rRPNClqxNxbTrxAKDvttzeBWr+OcWCFRYWdG9F5DNadxsLWsNRQwTikGww6Sgmnrkljo6d1H7PcilvpTuv6fC6PqtkkbaLqz7wpr/rEx+csErO65kjJbS2lbijTXgxT65JhjvD1iDrj5ArgHB16CotNUjN9B5zrLrz8hRIV0yr0laEWhftDPC5+OrMxYcqmK3UTBqtzJQOpsqWZKEIJaChC2Y9pLsoZ/sBwIDAQABAoIBABUGNH5SAjlpaQRkxWSGmlMoBc4w5wPP0xG4zszRbfBD1czEHezT8vzIek2BF8cp4jidpV8qlrHpLLgn7t0IZf7AHDcj4wwZDwZAxgf5ADQSf5Mh2grcc4wT717bGML7uUW922YV3Nqp664N40zy+E7MK6W/x/bdGlVWsl1D7/xnJM2IknNcxKB45SvjjPGbJu/SaqE0UlH1MBfTuDgmFG0xwCnS+lH7lrS4vo+/dE3aZARauvySyrEL5xQsv4DQmByRoo4GUsOivUH/5D4wYA+Dm1IZtxNcq/vVsmGLQxt6TFzPo7gr20IA/W/VsuXQeqTLdaoZjsaP8RQFbGv98zECgYEA3P+DLlaPQBhv4+AsW7/V7339EaHzP+qZSaCoVE1q3mFajf326OSRi63bSgBg7CxsI4W6j95uuJvLxV5P25bAOG8W7wIAz8oPLpJlQPOeZmVgbnB8KLauYoOKdNtyCVkfSqHsY67BsGa0mopnRJrtjOvi9jRB6S/6Gzj+g5lR1tUCgYEA1lsVjRWrscnbeOAlqcQ4JIM+3tkd8JceAIxW8L196u8ISa0gSfQGeuSwiostt3a/BKjFZSQ5cGvRzMqwGkBVXLbHGPuwL31SVh/7RQYakEinvInJacm38C3i7feTA2Hi2BsHvG1xvRIU9v8727aqgULX+HNEjB9eESrBkk9BHWsCgYEAligiCK0VnhY8iBd77EcW5Ce1eHKSZZ5P0sAPP2BuuXRqY8noJuuOnNpfAhPpxu6T9zrYvQIENvjcZlkjZ28xYebRLUouJQEEeb9MfupIeQhukftp0Pv21sbLn4SvIfzlDv+gL0bBIctW8R4S9oFR4Isx5dkx43AOvspl3CKjgZUCgYEAibp6jW04JYL6pp729C6kmClQMyW0DAs89sM1dXd7uYEehSBdF8dYhov8NviYRkJhF+BM/OCam3ZblkdBgYyGjIzQPmgxW0IdrkLcUwxJ8x0L0aOCq5s1uXfyUE57wneZppsvjE2SABbnK5DxaAnlYiqN1BBUIehhq4waViTgRMMCgYBwHvMOBt8OWgMsyN7p01ITK2QlTnzECOIj0ZcIi3XCDhLXgTo3m6lIhDStxp/5rFWGrNatZPSkD2ZMCo9oH+w93ISaiHnbxr0jttBvNwBPnJzZwKIBLNqmYPBYTJCbLsm7d5902RWC4YxEPGy7pG255m6jC8+b7nl+1oPR2FtLlA==-----END RSA PRIVATE KEY-----
-----BEGIN RSA PRIVATE KEY-----MIIEowIBAAKCAQEA2LemlIaaa8vbUHgDmdEafk3H/pXtFEO/UTuVdAi1go1lfflphQujdh1Htqgv/VA0jcZsOprjq9wl+juYxsUH+RH2cvSf2kIC5MY+X1gNp6NCm0+Zlvbz4XF7sJyuAH5UiRr1+QNd8kUbXtUHhmy5mRtKzC5jpPXZZcCHq5NcQfiw+SuyDzaCmrWuleorLME9TtkzWPu3CxgVvEOEE4Z2EjgTXbJ6NMe1wGRU1lD1d4gL/5DglvoyN6mdOSSeQzKNLdZrv3tgy3SAmM6sJwmS1ObkeC4tGskmgYzQ9MvZXVwRWE8xUr40F0PFN0oItU/SKr8hjWwHE5PX10Yl0MjImQIDAQABAoIBAD3nN431ZOaltF+n6F9ne0nYrefqq22+bEen3Wjnk/FWskbpl1qJmIeElZd3Mz4ISvq0UvXqiF3u5Go1283rOfvLRbpQZdjSQkFW3zoczMm1uLDka9rTb5ZV9B7eolVBwKPpL5mRfKRXWRodf6jGJb22LgdkuNHF5/NIq3g2/4NYH4xw8NCdL1/EcvZc/CveiyMoPlQFiCdOxuPLMmIYNsUZQLUI5EI/NBNOehtnbey0uDE7+PC7bVD01AZ8PYSfGezXHvHCJ9+6lQ0mF/PmopH2sOQ/kMBnuMxcO3c/E8fpNdGwOSDDyWg1PJ5lV/xnmm0sdV7/XXbW6J0zv4LzKIECgYEA9KIqUkTo5tpkZpfWmZ03hvknfR6FwTklCHz/wnKUuudyua2Y7NsROUanFdEmxDU8tOJVQT3ytV2MvJcINvcqsuTohBIwhsXUuAk5spwfA3Vk1peAAQ+tLBOepR+gc94k4MFY5ss1FyeqNx6cXKOqUvNQSPCYCJTH3AA2C3xR4PsCgYEA4slu0DvjtSySqoZkRbvO+iP6xZh+U7rhWnMXsUFmq3MxzCU/Ry5XqGuzb3Wb17Y5VNhAvA5biO+Gtc/WVOfdbLhJNCL+W4cfR8x5xfy2nXpLUHaN8Id+GFmDScLdWgYKJbgjN3rjHvW+r4YNo7sBhQ8UOgrSSsXZHpLYklyGEHsCgYEAv72HHFpkjeSpAvyJuHdQeVs6B0hwH8WRcDjBIgA68M/NzRjyntsJgfINrfzzvJ/ZiBFKL0vFuz+qunpKdwJ9lh/y2umC3W+bze91KLhTWpudwNCYBLzrx3tNQjEqywZXs034R1UItLBjKra0aaviKQgKalEhaMBscdQ8h/4WExcCgYA2Gbt3rXHKvJFYYKr2/7CGd6LRFGm+a6xquV4DiQiHCfntK02HG4UJxneNtU6yDORsWxJGSl6Hsiw+nxAQPSfTUbsU1uw6xWcu55Z9JqYhtxTUYxPFN21bPa9WH0hSu3IcQWsVRxl7P0B3+tCyKGBab5hxqDc2YzBCXOGROMU6lQKBgEFNOi0ifgraWJDk75au+PAVBGzIqsXZQn/ZqpWwWV43QaEkWQjrpRheEFiyVzPX+TMGcuzPXwWxed0BDUb0NBe0e1Lf9t10SOtLbkkm+KYsHxcgYEn+Tmp/VKiEUrwQi1jf2p5u9aTojBouOrCSYs8MMmYsyscbb823YS/NG7U+-----END RSA PRIVATE KEY-----
Enjoyed reading this content? Let the author know!
Your likes, comments, shares, and saves help creators reach more builders.

Loading recommendations
Loading article